AB 1859: Customer records.
- Session Year: 2017-2018
- House: Assembly
- Latest Version Date: 2018-09-19
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, or a 3rd party that maintains personal information about a California resident on behalf of a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information, to take certain measures to protect that data, including implementing software updates, if it knows or reasonably should know that a software update is available to address the security vulnerability, and employing reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified.
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, or a 3rd party that maintains personal information about a California resident on behalf of a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information, to take certain measures to protect that data, including implementing software updates, if it knows or reasonably should know that a software update is available to address the security vulnerability, and employing reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified.
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, or a 3rd party that maintains personal information about a California resident for on behalf of a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information, to take certain measures to protect that data, including implementing software updates, if it knows or reasonably should know that a software update is available to address the security vulnerability, and employing reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified.
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, or an entity that has a contract with a consumer credit reporting agency and a 3rd party that maintains personal information about a California resident on behalf of the for a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information, to take certain measures to protect that data, including implementing software updates, if it knows or reasonably should know that a software update is available to address the security vulnerability, and employing reasonable mitigation measures compensating controls to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified. The bill would authorize a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as specified, as a result of a breach of the security of the system caused, in whole or in part, by a security vulnerability that was not addressed as required, to institute a civil action to recover damages, civil penalties, and reasonable attorneys fees and costs for that injury. The bill would also authorize specified civil penalties to be recovered for a willful, intentional, or reckless violation of these provisions.
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, or an entity that has a contract with a consumer credit reporting agency and maintains personal information about a California resident on behalf of the consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a security vulnerability that could compromise poses a significant risk to the security of computerized data within the system that contains personal information, to take certain measures to protect that data, including implementing software updates, if it knows or reasonably should know that a software update is available to address a the security vulnerability, and employing reasonable mitigation measures to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified. The bill would authorize a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as specified, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system a security vulnerability that was not addressed as required, to institute a civil action to recover damages, a civil penalty, civil penalties, and reasonable attorneys fees and costs for that injury. The bill would also authorize specified civil penalties to be recovered for a willful, intentional, or reckless violation of these provisions.
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that conducts business in California, that owns, licenses, or maintains personal information about a California resident, that knows knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a vulnerability that could compromise the security of computerized data that contains personal information, and that also knows or reasonably should know that a software update is available to address that vulnerability, to apply that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 10 days after becoming aware of the vulnerability and the available software update. to take certain measures to protect that data, including implementing software updates, if it knows or reasonably should know that a software update is available to address a vulnerability, and employing reasonable mitigation measures to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified. The bill would authorize a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as specified, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system vulnerability to institute a civil action to recover damages, a civil penalty, and reasonable attorneys fees and costs for that injury. The bill would also authorize specified civil penalties to be recovered for a willful, intentional, or reckless violation of these provisions.
Existing law regulating consumer credit reporting agencies provides as its purpose to require, among other things, that these agencies adopt reasonable procedures for meeting the needs of commerce for consumer credit in a manner that is fair and equitable to the consumer with regard to the confidentiality of such information and in a manner that will best protect the interests of the people of the state. Existing law requires a person or business that owns or licenses computerized data that includes personal information to disclose any breach of the security of the system following discovery or notification of the breach in the security of the data to any resident of California whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person, or, whose encrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and the encryption key or security credential was, or is reasonably believed to have been, acquired by an unauthorized person and the agency that owns or licenses the encrypted information has a reasonable belief that the encryption key or security credential could render that personal information readable or useable. Existing law requires the disclosure to be made in the most expedient time possible and without unreasonable delay, as specified. Existing law authorizes any customer who is injured by a violation of these provisions to institute a civil action to recover damages.
This bill would require a consumer credit reporting agency that conducts business in California, that owns, licenses, or maintains personal information about a California resident, that knows or reasonably should know, that a computer system it owns, operates, or maintains is subject to a vulnerability that could compromise the security of computerized data that contains personal information, and that also knows or reasonably should know that a software update is available to address that vulnerability, to apply that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 10 days after becoming aware of the vulnerability and the available software update. The bill would authorize a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as specified, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system vulnerability to institute a civil action to recover damages, a civil penalty, and reasonable attorneys fees and costs for that injury. The bill would also authorize specified civil penalties to be recovered for a willful, intentional, or reckless violation of these provisions.
(a)A consumer credit reporting agency, as defined in 15 U.S.C. Sec. 1681a(p), that owns, licenses, or maintains personal information about a California resident, or a third party that maintains personal information about a California resident on behalf of a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk, as defined in subdivision (c), to the security of computerized data that contains personal information, as defined in subdivision (h) of Section 1798.82, shall do all of the following:
(1)If a consumer credit reporting agency knows or reasonably should know that a software update is available to address the vulnerability as described in subdivision (a), the agency shall begin the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update. The software update shall be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 90 days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update.
(2)Until the software update described in paragraph (1) is complete, the consumer credit reporting agency shall, in keeping with industry best practices, employ reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability as described in subdivision (a).
(b)Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do all of the following:
(1)Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited.
(2)Test and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data.
(3)Require, by contract, that the third party implement and maintain appropriate security measures for personal information. Contracting with a third party to maintain personal information about California residents shall not relieve the consumer credit agency of the requirements of this section.
(c)As used in this section, significant risk means a vulnerability score, calculated using a standard measurement system that is accepted as a best practice for the industry, to determine that the risk could reasonably result in a breach of the security of the system, as defined in subdivision (g) of Section 1798.82, of personal information, as defined in subdivision (h) of Section 1798.82.
(d)As used in this section, compensating controls means controls that the agency reasonably believes will prevent the computer system vulnerability as described in subdivision (a) from being exploited while the software update is being tested, assessed, and a plan for implementation is being developed, and have been adequately tested and confirmed to sufficiently offset the risk of breach caused by computer system vulnerability as described in subdivision (a).
(e)Nothing in this section shall reduce the responsibilities and obligations of a consumer credit reporting agency or third party under this title, including, but not limited to, Section 1798.81.5.
(f)The Attorney General has exclusive authority to enforce this section.
(a)A consumer credit reporting agency, as defined in 15 U.S.C. Sec. 1681a(p), that owns, licenses, or maintains personal information about a California resident, or a third party that maintains personal information about a California resident on behalf of a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk, as defined in subdivision (c), to the security of computerized data that contains personal information, as defined in subdivision (h) of Section 1798.82, shall do all of the following:
(1)If a consumer credit reporting agency knows or reasonably should know that a software update is available to address the vulnerability as described in subdivision (a), the agency shall begin the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update. The software update shall be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 90 days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update.
(2)Until the software update described in paragraph (1) is complete, the consumer credit reporting agency shall, in keeping with industry best practices, employ reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability as described in subdivision (a).
(b)Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do all of the following:
(1)Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited.
(2)Test and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data.
(3)Require, by contract, that the third party implement and maintain appropriate security measures for personal information. Contracting with a third party to maintain personal information about California residents shall not relieve the consumer credit agency of the requirements of this section.
(c)As used in this section, significant risk means a vulnerability score, calculated using a standard measurement system that is accepted as a best practice for the industry, to determine that the risk could reasonably result in a breach of the security of the system, as defined in subdivision (g) of Section 1798.82, of personal information, as defined in subdivision (h) of Section 1798.82.
(d)As used in this section, compensating controls means controls that the agency reasonably believes will prevent the computer system vulnerability as described in subdivision (a) from being exploited while the software update is being tested, assessed, and a plan for implementation is being developed, and have been adequately tested and confirmed to sufficiently offset the risk of breach caused by computer system vulnerability as described in subdivision (a).
(e)Nothing in this section shall reduce the responsibilities and obligations of a consumer credit reporting agency or third party under this title, including, but not limited to, Section 1798.81.5.
(f)The Attorney General has exclusive authority to enforce this section.
(a)A consumer credit reporting agency, as defined in 15 U.S.C. Sec. 1681a(p), that owns, licenses, or maintains personal information about a California resident, or a third party that maintains personal information about a California resident for on behalf of a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk risk, as defined in subdivision (c), to the security of computerized data, as defined in subdivision(d), data that contains personal information, as defined in subdivision (h) of Section 1798.82, shall do all of the following:
(1)If a consumer credit reporting agency knows or reasonably should know that a software update is available to address the vulnerability as described in subdivision (a), the agency shall begin the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update. The software update shall be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 90 days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update.
(2)Until the software update described in paragraph (1) is complete, the consumer credit reporting agency shall, in keeping with industry best practices, employ reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability as described in subdivision (a).
(b)Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do all of the following:
(1)Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited.
(2)Test and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data.
(3)Require, by contract, that the third party implement and maintain appropriate security measures for personal information. Contracting with a third party to maintain personal information about California residents shall not relieve the consumer credit agency of the requirements of this section.
(c)A third party shall notify the consumer credit reporting agency of any known vulnerabilities as expeditiously as possible, but in any event, within two days.(d)(c)As used in this section, significant risk means a vulnerability score, calculated using a standard measurement system that is accepted as a best practice for the industry, to determine that the risk could reasonably result in a breach of the security of the system, as defined in subdivision (g) of Section 1798.82, of personal information, as defined in subdivision (h) of Section 1798.82.
(e)(d)As used in this section, compensating controls means controls that the agency reasonably believes will prevent the computer system vulnerability as described in subdivision (a) from being exploited while the software update is being tested, assessed, and a plan for implementation is being developed, and have been adequately tested and confirmed to sufficiently offset the risk of breach caused by computer system vulnerability as described in subdivision (a).
(f)(e)Nothing in this section shall reduce the responsibilities and obligations of a consumer credit reporting agency or third party under this title, including, but not limited to, Section 1798.81.5.
(g)(f)The Attorney General has exclusive authority to enforce this section.
(a)A consumer credit reporting agency agency, as defined in 15 U.S.C. Sec. 1681a(p), that owns, licenses, or maintains personal information about a California resident, or an entity that has a contract with a consumer credit reporting agency and maintains personal information about a California resident on behalf of the consumer credit reporting agency, a third party that maintains personal information about a California resident for a consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains maintains, and for which it controls the security protocols, is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system data, as defined in subdivision(d), that contains personal information, as defined in subdivision (h) of Section 1798.82, shall do all of the following:
(1)If a consumer credit reporting agency knows or reasonably should know that a software update is available to address the vulnerability as described in subdivision (a), the agency shall begin to implement the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update. The software update shall be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 30 90 days after becoming aware aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update.
(2)Until the software update described in paragraph (1) is complete, the consumer credit reporting agency shall, in keeping with industry best practices, employ reasonable mitigation measures compensating controls to reduce the risk of a breach caused by computer system vulnerability as described in subdivision (a).
(3)(b)Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do both all of the following:
(A)(1)Identify, prioritize, and address the highest-risk highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited.
(B)(2)Test the impact of mitigation measures and software updates on its computer system and how they effect and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data.
(3)Require, by contract, that the third party implement and maintain appropriate security measures for personal information. Contracting with a third party to maintain personal information about California residents shall not relieve the consumer credit agency of the requirements of this section.
(c)A third party shall notify the consumer credit reporting agency of any known vulnerabilities as expeditiously as possible, but in any event, within two days.
(b)A resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as described in subdivision (a) of Section 1798.82, as a result of a breach of the security of the system caused, in whole or in part, by a security vulnerability that was not addressed, as required, by subdivision (a) is deemed to have suffered an injury in fact, and, therefore, may recover a civil penalty for each breach of the security of the system, damages, and reasonable attorneys fees and costs pursuant to Section 1798.84 in addition to any other rights or remedies provided by law.(c)(d)As used in this section, significant risk means a vulnerability score, calculated using a standard measurement system used by industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk. could reasonably result in a breach of the security of the system, as defined in subdivision (g) of Section 1798.82, of personal information, as defined in subdivision (h) of Section 1798.82.
(e)As used in this section, compensating controls means controls that the agency reasonably believes will prevent the computer system vulnerability as described in subdivision (a) from being exploited while the software update is being tested, assessed, and a plan for implementation is being developed, and have been adequately tested and confirmed to sufficiently offset the risk of breach caused by computer system vulnerability as described in subdivision (a).
(f)Nothing in this section shall reduce the responsibilities and obligations of a consumer credit reporting agency or third party under this title, including, but not limited to, Section 1798.81.5.
(g)The Attorney General has exclusive authority to enforce this section.
SEC. 2.Section 1798.84 of the Civil Code is amended to read:1798.84.(a)Any waiver of a provision of this title is contrary to public policy and is void and unenforceable.(b)A customer or a resident, as described in subdivision (b) of Section 1798.81.6, injured by a violation of this title may institute a civil action to recover damages.(c)In addition, for a willful, intentional, or reckless violation of Section 1798.81.6 or 1798.83, a customer or resident may recover a civil penalty not to exceed three thousand dollars ($3,000) per violation; otherwise, the customer or resident may recover a civil penalty of up to five hundred dollars ($500) per violation for a violation of Section 1798.81.6 or 1798.83.(d)Unless the violation is willful, intentional, or reckless, a business that is alleged to have not provided all the information required by subdivision (a) of Section 1798.83, to have provided inaccurate information, failed to provide any of the information required by subdivision (a) of Section 1798.83, or failed to provide information in the time period required by subdivision (b) of Section 1798.83, may assert as a complete defense in any action in law or equity that it thereafter provided regarding the information that was alleged to be untimely, all the information, or accurate information, to all customers who were provided incomplete or inaccurate information, respectively, within 90 days of the date the business knew that it had failed to provide the information, timely information, all the information, or the accurate information, respectively.(e)Any business that violates, proposes to violate, or has violated this title may be enjoined.(f)(1)A cause of action shall not lie against a business for disposing of abandoned records containing personal information by shredding, erasing, or otherwise modifying the personal information in the records to make it unreadable or undecipherable through any means.(2)The Legislature finds and declares that when records containing personal information are abandoned by a business, they often end up in the possession of a storage company or commercial landlord. It is the intent of the Legislature in paragraph (1) to create a safe harbor for such a record custodian who properly disposes of the records in accordance with paragraph (1).(g)A prevailing plaintiff in any action commenced under Section 1798.81.6 or 1798.83 shall also be entitled to recover his or her reasonable attorneys fees and costs.(h)The rights and remedies available under this section are cumulative to each other and to any other rights and remedies available under law.(a)A consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, or an entity that has a contract with a consumer credit reporting agency and maintains personal information about a California resident on behalf of the consumer credit reporting agency, that knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a security vulnerability that could compromise poses a significant risk to the security of computerized data within the system that contains personal information, as defined in subdivision (h) of Section 1798.82, shall do both all of the following:
(1)A If a consumer credit reporting agency that knows or reasonably should know that a software update is available to address a the vulnerability as described in subdivision (a), the agency shall begin to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 3 no later than three business days after becoming aware of the vulnerability and the available software update. The installation software update shall be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within no later than 30 days after becoming aware of the vulnerability and the available software update.
(2)Until the software update described in paragraph (1) is complete, the consumer credit reporting agency shall, in keeping with industry best practices, employ reasonable mitigation measures to reduce the risk of a breach caused by computer system vulnerability as described in subdivision (a).
(3)Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do both of the following:
(A)Identify, prioritize, and address the highest-risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited.
(B)Test the impact of mitigation measures and software updates on its computer system and how they effect the vulnerability of the system to threats to the security of computerized data.
(b)A resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as described in subdivision (a) of Section 1798.82, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system a security vulnerability in violation of that was not addressed, as required, by subdivision (a) is deemed to have suffered an injury in fact, and, therefore, may recover a civil penalty for each breach of the security of the system, damages, and reasonable attorneys fees and costs pursuant to Section 1798.84 in addition to any other rights or remedies provided by law.
(c)As used in this section, significant risk means a vulnerability score, calculated using a standard measurement system used by industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk.
SEC. 2.Section 1798.84 of the Civil Code is amended to read:1798.84.(a)Any waiver of a provision of this title is contrary to public policy and is void and unenforceable.
(b)A customer or a resident, as described in subdivision (b) of Section 1798.81.6, injured by a violation of this title may institute a civil action to recover damages.
(c)In addition, for a willful, intentional, or reckless violation of Section 1798.81.6 or 1798.83, a customer or resident may recover a civil penalty not to exceed three thousand dollars ($3,000) per violation; otherwise, the customer or resident may recover a civil penalty of up to five hundred dollars ($500) per violation for a violation of Section 1798.81.6 or 1798.83.
(d)Unless the violation is willful, intentional, or reckless, a business that is alleged to have not provided all the information required by subdivision (a) of Section 1798.83, to have provided inaccurate information, failed to provide any of the information required by subdivision (a) of Section 1798.83, or failed to provide information in the time period required by subdivision (b) of Section 1798.83, may assert as a complete defense in any action in law or equity that it thereafter provided regarding the information that was alleged to be untimely, all the information, or accurate information, to all customers who were provided incomplete or inaccurate information, respectively, within 90 days of the date the business knew that it had failed to provide the information, timely information, all the information, or the accurate information, respectively.
(e)Any business that violates, proposes to violate, or has violated this title may be enjoined.
(f)(1)A cause of action shall not lie against a business for disposing of abandoned records containing personal information by shredding, erasing, or otherwise modifying the personal information in the records to make it unreadable or undecipherable through any means.
(2)The Legislature finds and declares that when records containing personal information are abandoned by a business, they often end up in the possession of a storage company or commercial landlord. It is the intent of the Legislature in paragraph (1) to create a safe harbor for such a record custodian who properly disposes of the records in accordance with paragraph (1).
(g)A prevailing plaintiff in any action commenced under Section 1798.81.6 or 1798.83 shall also be entitled to recover his or her reasonable attorneys fees and costs.
(h)The rights and remedies available under this section are cumulative to each other and to any other rights and remedies available under law.
(a)A consumer credit reporting agency that conducts business in California, that owns, licenses, or maintains personal information about a California resident, that knows knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a vulnerability that could compromise the security of computerized data that contains personal information, as defined in subdivision (h) of Section 1798.82, and that also knows or reasonably should know that a software update is available to address that vulnerability, shall apply that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 10 days after becoming aware of the vulnerability and the available software update. shall do both of the following:
(1)A consumer credit reporting agency that knows or reasonably should know that a software update is available to address a vulnerability as described in subdivision (a), shall begin to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 3 business days after becoming aware of the vulnerability and the available software update. The installation shall be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 30 days after becoming aware of the vulnerability and the available software update.
(2)Until the software update described in paragraph (1) is complete, the consumer credit reporting agency shall, in keeping with industry best practices, employ reasonable mitigation measures to reduce the risk of a breach caused by computer system vulnerability as described in subdivision (a).
(b)A resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as described in subdivision (a) of Section 1798.82, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system vulnerability in violation of subdivision (a) has is deemed to have suffered an injury in fact, and and, therefore, may recover a civil penalty and reasonable attorneys fees and costs pursuant to Section 1798.84 in addition to any other rights or remedies provided by law.
SEC. 2.Section 1798.84 of the Civil Code is amended to read:1798.84.(a)Any waiver of a provision of this title is contrary to public policy and is void and unenforceable.
(b)A customer or a resident, as described in subdivision (b) of Section 1798.81.6, injured by a violation of this title may institute a civil action to recover damages.
(c)In addition, for a willful, intentional, or reckless violation of Section 1798.81.6 or 1798.83, a customer may recover a civil penalty not to exceed three thousand dollars ($3,000) per violation; otherwise, the customer may recover a civil penalty of up to five hundred dollars ($500) per violation for a violation of Section 1798.81.6 or 1798.83.
(d)Unless the violation is willful, intentional, or reckless, a business that is alleged to have not provided all the information required by subdivision (a) of Section 1798.83, to have provided inaccurate information, failed to provide any of the information required by subdivision (a) of Section 1798.83, or failed to provide information in the time period required by subdivision (b) of Section 1798.83, may assert as a complete defense in any action in law or equity that it thereafter provided regarding the information that was alleged to be untimely, all the information, or accurate information, to all customers who were provided incomplete or inaccurate information, respectively, within 90 days of the date the business knew that it had failed to provide the information, timely information, all the information, or the accurate information, respectively.
(e)Any business that violates, proposes to violate, or has violated this title may be enjoined.
(f)(1)A cause of action shall not lie against a business for disposing of abandoned records containing personal information by shredding, erasing, or otherwise modifying the personal information in the records to make it unreadable or undecipherable through any means.
(2)The Legislature finds and declares that when records containing personal information are abandoned by a business, they often end up in the possession of a storage company or commercial landlord. It is the intent of the Legislature in paragraph (1) to create a safe harbor for such a record custodian who properly disposes of the records in accordance with paragraph (1).
(g)A prevailing plaintiff in any action commenced under Section 1798.83 shall also be entitled to recover his or her reasonable attorneys fees and costs.
(h)The rights and remedies available under this section are cumulative to each other and to any other rights and remedies available under law.
(a)A consumer credit reporting agency that conducts business in California, that owns, licenses, or maintains personal information about a California resident, that knows or reasonably should know, that a computer system it owns, operates, or maintains is subject to a vulnerability that could compromise the security of computerized data that contains personal information, as defined in subdivision (h) of Section 1798.82, and that also knows or reasonably should know that a software update is available to address that vulnerability, shall apply that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 10 days after becoming aware of the vulnerability and the available software update.
(b)A resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as described in subdivision (a) of Section 1798.82, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system vulnerability in violation of subdivision (a) has suffered an injury in fact, and may recover a civil penalty and reasonable attorneys fees and costs pursuant to Section 1798.84 in addition to any other rights or remedies provided by law.
SEC. 2.Section 1798.84 of the Civil Code is amended to read:1798.84.(a)Any waiver of a provision of this title is contrary to public policy and is void and unenforceable.
(b)Any A customer or a resident, as described in subdivision (b) of Section 1798.81.6, injured by a violation of this title may institute a civil action to recover damages.
(c)In addition, for a willful, intentional, or reckless violation of Section 1798.81.6 or 1798.83, a customer may recover a civil penalty not to exceed three thousand dollars ($3,000) per violation; otherwise, the customer may recover a civil penalty of up to five hundred dollars ($500) per violation for a violation of Section 1798.83. 1798.81.6 or 1798.83.
(d)Unless the violation is willful, intentional, or reckless, a business that is alleged to have not provided all the information required by subdivision (a) of Section 1798.83, to have provided inaccurate information, failed to provide any of the information required by subdivision (a) of Section 1798.83, or failed to provide information in the time period required by subdivision (b) of Section 1798.83, may assert as a complete defense in any action in law or equity that it thereafter provided regarding the information that was alleged to be untimely, all the information, or accurate information, to all customers who were provided incomplete or inaccurate information, respectively, within 90 days of the date the business knew that it had failed to provide the information, timely information, all the information, or the accurate information, respectively.
(e)Any business that violates, proposes to violate, or has violated this title may be enjoined.
(f)(1)A cause of action shall not lie against a business for disposing of abandoned records containing personal information by shredding, erasing, or otherwise modifying the personal information in the records to make it unreadable or undecipherable through any means.
(2)The Legislature finds and declares that when records containing personal information are abandoned by a business, they often end up in the possession of a storage company or commercial landlord. It is the intent of the Legislature in paragraph (1) to create a safe harbor for such a record custodian who properly disposes of the records in accordance with paragraph (1).
(g)A prevailing plaintiff in any action commenced under Section 1798.83 shall also be entitled to recover his or her reasonable attorneys fees and costs.
(h)The rights and remedies available under this section are cumulative to each other and to any other rights and remedies available under law.
|
Date
|
Status
|
|---|---|
| Sep 19, 2018 | Chaptered by Secretary of State - Chapter 532, Statutes of 2018. |
| Sep 19, 2018 | Approved by the Governor. |
| Sep 6, 2018 | Enrolled and presented to the Governor at 3 p.m. |
| Aug 29, 2018 | Senate amendments concurred in. To Engrossing and Enrolling. |
| Aug 27, 2018 | In Assembly. Concurrence in Senate amendments pending. May be considered on or after August 29 pursuant to Assembly Rule 77. |
| Aug 27, 2018 | Read third time. Passed. Ordered to the Assembly. |
| Aug 23, 2018 | Read second time. Ordered to third reading. |
| Aug 22, 2018 | Read third time and amended. Ordered to second reading. |
| Aug 20, 2018 | Read second time. Ordered to third reading. |
| Aug 17, 2018 | From committee: Amend, and do pass as amended. (Ayes 5. Noes 2.) (August 16). |
| Aug 6, 2018 | In committee: Referred to APPR. suspense file. |
| Jun 27, 2018 | From committee: Do pass and re-refer to Com. on APPR. (Ayes 5. Noes 2.) (June 26). Re-referred to Com. on APPR. |
| Jun 13, 2018 | Referred to Coms. on JUD. and APPR. |
| Jun 4, 2018 | In Senate. Read first time. To Com. on RLS. for assignment. |
| May 31, 2018 | Read third time. Passed. Ordered to the Senate. |
| May 7, 2018 | Read second time. Ordered to third reading. |
| May 3, 2018 | Read second time and amended. Ordered returned to second reading. |
| May 2, 2018 | From committee: Amend, and do pass as amended. (Ayes 8. Noes 2.) (May 1). |
| Apr 23, 2018 | Re-referred to Com. on JUD. |
| Apr 19, 2018 | Read second time and amended. |
| Apr 18, 2018 | From committee: Amend, and do pass as amended and re-refer to Com. on JUD. (Ayes 9. Noes 1.) (April 17). |
| Apr 2, 2018 | In committee: Hearing postponed by committee. |
| Jan 29, 2018 | Referred to Coms. on P. & C.P. and JUD. |
| Jan 11, 2018 | From printer. May be heard in committee February 10. |
| Jan 10, 2018 | Read first time. To print. |
|
Date
|
Description
|
Location
|
Votes
|
|
|---|---|---|---|---|
| Aug 29, 2018 | AB 1859 CHAU Concurrence in Senate Amendments | Assembly Floor |
Passed |
|
| Aug 27, 2018 | Assembly 3rd Reading AB1859 Chau By Hertzberg | Senate Floor |
Passed |
|
| Aug 16, 2018 | Do pass as amended | Senate Standing Committee on Appropriations |
Passed |
|
| Aug 6, 2018 | Placed on suspense file | Senate Standing Committee on Appropriations |
Passed |
|
| Jun 26, 2018 | Do pass, but first be re-referred to the Committee on [Appropriations] | Senate Standing Committee on Judiciary |
Passed |
|
| May 31, 2018 | AB 1859 CHAU Assembly Third Reading | Assembly Floor |
Passed |
|
| May 1, 2018 | Do pass as amended. | Assembly Standing Committee on Judiciary |
Passed |
|
| Apr 17, 2018 | Do pass as amended and be re-referred to the Committee on [Judiciary] | Assembly Standing Committee on Privacy and Consumer Protection |
Passed |
This list shows positions taken on this bill by organizations on the date displayed, which is linked to the original source.
Positions by individuals are not included.
|
Organization
|
Position
|
Date
|
|---|---|---|
| ACLU of California | * Indeterminate | May 1, 2018 |
| California Association Of Collectors | ** Against | Aug 20, 2018 |
| California Low-Income Consumer Coalition | ** Support | Aug 23, 2018 |
| Civil Justice Association Of California | * Against | May 1, 2018 |
| Consumer Data Industry Association | ** Against | Aug 20, 2018 |
| Experian Credit Reporting Agency | * Against | May 1, 2018 |
| Insurance Commissioner Dave Jones | ** Support | Aug 23, 2018 |
| Neutral | ** Against | Apr 29, 2018 |
| Privacy Rights Clearinghouse | ** Support | Aug 23, 2018 |
CONCURRENCE IN SENATE AMENDMENTS
CSA1 Bill Id:AB 1859
Author:(Chau)
As Amended Ver:August 22, 2018
Majority vote
ASSEMBLY: | 57-15 | (May 31, 2018) | SENATE: | 39-0 | (August 27, 2018) |
Original Committee Reference: P. & C.P.
SUMMARY: This bill requires consumer credit reporting agencies (CCRAs) and affiliated third parties that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of computerized data containing personal information to begin the process of implementing available software updates in a timely manner, as specified. Specifically, this bill:
- Requires a CCRA that knows or reasonably should know that a software update is available to address a vulnerability that poses a significant risk to the security of computerized data containing personal information, to begin the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware of the vulnerability and the available software update, as specified.
- Requires the software update to be completed in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 90 days after becoming aware of the vulnerability and the available software update, as specified.
- Requires a CCRA to employ reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability until the software update is completed.
- Requires CCRAs, notwithstanding whether a software update is available, to do the following:
- Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited.
- Test and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data.
- Require, by contract, that the third party implement and maintain appropriate security measures for personal information, as specified.
- Defines, for the purposes of this section "significant risk" and "compensating controls".
- Provides that the Attorney General has exclusive authority to enforce this section.
The Senate amendments clarified which entities would be considered a third party for the purposes of the bill, created a duty for a CCRA that "reasonably should have been aware" of a vulnerability and available software update, granted exclusive authority to enforce the bill to the Attorney General, and made other clarifying and technical changes.
FISCAL EFFECT: Unknown
COMMENTS: According to the author, "According to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers' personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats. That is what this bill attempts to do."
Recognizing that premature installation of a software update or patch could have the unintended consequence of undermining the security of the software it seeks to secure, this bill creates a flexible approach by which CCRAs are required to assess risk, prioritize vulnerabilities, and allows CCRAs to property test, plan, and assess its systems prior to the implementation of an available software update. Further protecting consumers, this bill would require CCRAs to employ reasonable compensating controls to reduce the risk of a breach caused by computer system vulnerability until a software update is complete, and would require other routine testing and evaluating of compensating controls and how they affect the vulnerability of the system.
The California Low-Income Consumer Coalition writes in support: "CCRAs assemble consumer financial information for the purpose of issuing credit reports to third parties. The credit reports contain a historical record of the debts and associated payment information of individuals. Credit file information, which helps generate a score, is most commonly used to help lenders assess the risk of potential borrowers when underwriting a loan. Credit reports are also used by landlords when evaluating potential tenants and by employers when evaluating potential employees. These reports and the data contained therein need enhanced protections given the potential challenges consumers may face in the event of a beach. . . . AB 1859 updates our law to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats."
This bill has no opposition.
Analysis Prepared by: Nichole Rapier / P. & C.P. / (916) 319-2200 FN: 0004989
Office of Senate Floor Analyses (916) 651-1520 Fax: (916) 327-4478 | AB |
THIRD READING
Bill No: AB 1859
:
SENATE JUDICIARY COMMITTEE: 5-2, 6/26/18
AYES: Jackson, Hertzberg, Monning, Stern, Wieckowski
NOES: Moorlach, Anderson
SENATE APPROPRIATIONS COMMITTEE: 5-2, 8/16/18
AYES: Portantino, Beall, Bradford, Hill, Wiener
NOES: Bates, Nielsen
ASSEMBLY FLOOR: 57-15, 5/31/18 - See last page for vote
DIGEST:
This bill places requirements on consumer credit reporting agencies, and affiliated third parties, that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of computerized data containing personal information. Requires such entities to begin the process of implementation of software updates, if available, in a timely manner, and to identify and respond to security vulnerabilities in order to mitigate the attendant risks, as specified.
Senate Floor Amendments of 8/22/18 remove the requirement that third parties notify consumer credit reporting agencies of known vulnerabilities as expeditiously as possible, but in any event, within two days; and make technical changes.
Existing law:
- Declares, pursuant to the Information Practices Act of 1977, that the right to privacy is a personal and fundamental right protected by article I, section 1 of the Constitution of California and by the United States Constitution, and that all individuals have a right of privacy in information pertaining to them. (Civ. Code Sec. 1798 et seq.)
- Provides, through the California Customer Records Act, requirements for the maintenance and disposal of customer records and the personal information contained therein. (Civ. Code Sec. 1798.80 et seq.)
- Requires a business that owns, licenses, or maintains personal information about a California resident to implement and maintain reasonable security procedures and practices appropriate to the nature of the information, to protect the personal information from unauthorized access, destruction, use, modification, or disclosure and requires such businesses to contractually require nonaffiliated third parties to which it discloses such personal information to similarly protect that information. (Civ. Code Sec. 1798.81.5(b), (c).)
- Requires, through the data breach notification law, that any agency, person, or business that owns or licenses computerized data that includes personal information to disclose a breach of the security of the system to any California resident whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person. The disclosure must be made in the most expedient time possible and without unreasonable delay, consistent with the legitimate needs of law enforcement, as specified. (Civ. Code Secs. 1798.29(a), (c) and 1798.82(a), (c).)
- Requires any agency, person, or business that maintains computerized data that includes personal information that the agency, person, or business does not own to notify the owner or licensee of the information of any security breach immediately following discovery if the personal information was, or is reasonably believed to have been, acquired by an unauthorized person. (Civ. Code Secs. 1798.29(b), 1798.82(b).) “Personal information” for the purposes of these provisions, means either of the following:
- an individual’s first name or first initial and the individual’s last name in combination with one or more specified data elements, such as social security number, medical information, health insurance information, or credit card number, when either the name or the data elements are not encrypted or redacted; or
- a username or email address in combination with a password or security question and answer that would permit access to an online account. (Civ. Code Secs. 1798.29(g) and (h); 1798.82(h) and (i).)
- Provides that an agency, person or business that is required to issue a security breach notification shall meet specified requirements. The notification must be written in plain language, meet certain type and format requirements, and titled “Notice of Data Breach.” The security breach notification is required to include, specified information, including a list of the types of personal information that were or are reasonably believed to have been the subject of a breach and a general description of the breach incident, if that information is possible to determine at the time the notice is provided. (Civ. Code Secs. 1798.29(d), 1798.82(d).)
- Declares any waiver of the provisions of the California Customer Records Act contrary to public policy and void and unenforceable. It provides any customer injured by a violation of these provisions a civil right of action to recover damages and authorizes injunctive relief against such businesses. Any business that violates, proposes to violate, or has violated this title may be enjoined. (Civ. Code Sec. 1798.84.)
- Provides that for a willful, intentional, or reckless violation of Section 1798.83, governing the sharing of personal information with third parties, a customer may recover a civil penalty not to exceed $3,000 per violation; otherwise, the customer may recover a civil penalty of up to $500 per violation for a violation of Section 1798.83. A prevailing plaintiff in any action commenced under Section 1798.83 shall also be entitled to recover his or her reasonable attorney’s fees and costs. (Civ. Code Sec. 1798.84.)
This bill:
- Provides that a consumer credit reporting agency (CCRA), as defined, that owns, licenses, or maintains personal information about a California resident, or a third party that maintains such information on behalf of the CCRA, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, as defined, is subject to a security vulnerability that poses a significant risk to the security of computerized data that contains personal information, as defined, shall do all of the following:
- if a CCRA knows or reasonably should know that a software update is available to address the vulnerability, it shall begin the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update. The software update shall be completed in the same manner, but in any case no later than 90 days thereafter;
- until the software update is complete, the CCRA shall employ reasonable compensating controls, as defined, to reduce the risk of a breach caused by the vulnerability; and
- notwithstanding whether a software update is available, the CCRA shall identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited. It must also test and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data and must contractually require that the third party implement and maintain appropriate security measures for personal information.
- Provides that the Attorney General has exclusive authority to enforce this section.
- Defines “significant risk” as a vulnerability score, calculated using a standard measurement system that is accepted as a best practice for the industry, to determine that the risk could reasonably result in a breach of the security of the system of personal information.
Background
“If you have a credit report, there’s a good chance that you’re one of the 143 million American consumers whose sensitive personal information was exposed in a data breach at Equifax, one of the nation’s three major credit reporting agencies.” (Seena Gressin, The Equifax Data Breach: What to Do (Sep. 9, 2017) Federal Trade Commission <https://www.consumer.ftc.gov/blog/2017/09/equifax-data-breach-what-do [as of June 4, 2018].) The infamous breach at Equifax lasted at least several months in 2017. The hackers involved were able to access people’s names, Social Security numbers, birth dates, addresses, and driver’s license numbers. Over 200,000 consumers also had their credit card numbers stolen.
There is evidence that the massive hack of personal information has led to extensive identity theft with the thieves using the stolen information to apply for mortgages, credit cards, and student loans. The information is also being used to tap into bank accounts, to file insurance claims, and to incur massive debts on behalf of affected consumers. A nation-wide class action suit has been filed against Equifax, Allen et al. v. Equifax, which alleges the company “failed spectacularly” in its legal responsibilities to protect consumers’ confidential data. It also alleges that the company failed to take steps to upgrade its security protocols, such as installing a remedial patch provided by a software maker, and then delayed informing consumers about the breach, thereby preventing them from taking steps to minimize the damage.
Recently, Equifax’s former chief executive officer admitted that the company did not meet its responsibility to protect sensitive consumer information, confirming that the failure to fix a software vulnerability led to the massive, unprecedented theft of personal data. The company was using open source Apache software. Months before hackers breached Equifax’s system, the Apache Software Foundation issued a “patch” to address the security vulnerability in the software.
In fact, the Department of Homeland Security specifically notified Equifax of the vulnerability in its software and the need for the patch. Following up on this, the company’s own security team required the vulnerability be patched with 48 hours. That never happened, and, as a result, half of the people in the United States had their personal information stolen.
This bill places requirements on consumer credit reporting agencies, and affiliated third parties, that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of the data it contains. Such entities are required to begin to implement software updates, if available, in a timely manner, and to identify and respond to security vulnerabilities in order to mitigate the attendant risks.
Comments
The author writes:
According to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers’ personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats.
AB 1859 attempts to do this by requiring a CCRA conducting business in California to begin to implement a patch of its computer system within three days, and then complete the installation within the most expedient time possible, consistent with industry best practices, but no longer than [90] days in any case, if it is subject to a vulnerability that could compromise the security of computerized data containing personal information
Ensuring security vulnerabilities are addressed in a timely and effective manner
California recognizes that the right to privacy is a fundamental right, and has enshrined that right along with other fundamental rights in Article I, Section 1 of the California Constitution.
Unfortunately, because of the size of its economy and the sheer number of consumers, the data collected and held by California businesses is frequently targeted by cyber criminals. Over the four-year period from 2012 to 2015, the Attorney General received reports on over 657 breaches, affecting over 49 million records. (California Department of Justice, California Data Breach Report (Feb. 2016) <https://oag.ca.gov/breachreport 2016 [as of June 7, 2018].) In 2015 alone, nearly three in five Californians were victims of a data breach. These data breaches are not harmless. The Attorney General reports that in 2014, 67 percent of breach victims in the United States were also victims of fraud.
Existing law requires businesses that own, license, or maintain certain personal information to implement and maintain reasonable security procedures and practices to protect that information. (Civ. Code Sec. 1798.81.5.) In the event that such personal information of a California resident has been acquired by an unauthorized person, the responsible business is required to disclose such a breach to the affected person in the most expedient time possible and without unreasonable delay. (Civ. Code Sec. 1798.82.)
This bill builds on this statutory scheme. It requires CCRAs, and affiliated third parties, that handle the personal information of California residents to address security vulnerabilities that they know, or reasonably should know, exist. It requires these entities to take action in a reasonably timely manner, as specified, in response to such threats. It also requires these companies to proactively mitigate the security issues and to prioritize and address the vulnerabilities, regardless of the availability of a “patch” for the software.
This is a modest, commonsense requirement that should arguably already be taking place as part of baseline information security. Furthermore, it narrowly targets security risks that pose a “significant risk.” This bill helps to ensure that there is not another easily preventable breach like that in the Equifax context. However, the bill places exclusive authority for enforcement with the Attorney General and does not enable consumers to enforce the protections this bill affords them on their own.
FISCAL EFFECT: Appropriation: Fiscal Com.: Local:
According to the Senate Appropriations Committee, negligible fiscal impact to the state.
Insurance Commissioner Dave Jones
California Low-Income Consumer Coalition
Privacy Rights Clearinghouse
OPPOSITION: (Verified 8/23/18)
None received
ARGUMENTS IN SUPPORT: The California Low-Income Consumer Coalition writes in support: “CCRAs assemble consumer financial information for the purpose of issuing credit reports to third parties. The credit reports contain a historical record of the debts and associated payment information of individuals. Credit file information, which helps generate a score, is most commonly used to help lenders assess the risk of potential borrowers when underwriting a loan. Credit reports are also used by landlords when evaluating potential tenants and by employers when evaluating potential employees. These reports and the data contained therein need enhanced protections given the potential challenges consumers may face in the event of a beach. . . . AB 1859 updates our law to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats.”
ASSEMBLY FLOOR: 57-15, 5/31/18
AYES: Acosta, Aguiar-Curry, Arambula, Baker, Berman, Bloom, Bonta, Burke, Caballero, Calderon, Carrillo, Cervantes, Chau, Chiu, Chu, Cooley, Cooper, Daly, Eggman, Frazier, Friedman, Cristina Garcia, Eduardo Garcia, Gipson, Gloria, Gonzalez Fletcher, Gray, Grayson, Holden, Irwin, Jones-Sawyer, Kalra, Kamlager-Dove, Lackey, Levine, Limón, Low, Maienschein, McCarty, Medina, Melendez, Mullin, Muratsuchi, Nazarian, Obernolte, Quirk, Reyes, Rodriguez, Salas, Santiago, Mark Stone, Thurmond, Ting, Waldron, Weber, Wood, Rendon
NOES: Travis Allen, Bigelow, Brough, Chávez, Cunningham, Flora, Fong, Gallagher, Harper, Kiley, Mathis, Mayes, Patterson, Steinorth, Voepel
NO VOTE RECORDED: Chen, Choi, Dahle, O'Donnell, Quirk-Silva, Rubio
8/23/18 17:33:17
**** END ****
Office of Senate Floor Analyses (916) 651-1520 Fax: (916) 327-4478 | AB |
THIRD READING
Bill No: AB 1859
:
SENATE JUDICIARY COMMITTEE: 5-2, 6/26/18
AYES: Jackson, Hertzberg, Monning, Stern, Wieckowski
NOES: Moorlach, Anderson
SENATE APPROPRIATIONS COMMITTEE: 5-2, 8/16/18
AYES: Portantino, Beall, Bradford, Hill, Wiener
NOES: Bates, Nielsen
ASSEMBLY FLOOR: 57-15, 5/31/18 - See last page for vote
DIGEST:
This bill places requirements on consumer credit reporting agencies, and affiliated third parties, that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of computerized data containing personal information. Requires such entities to begin the process of implementation of software updates, if available, in a timely manner, and to identify and respond to security vulnerabilities in order to mitigate the attendant risks, as specified.
Existing law:
- Declares, pursuant to the Information Practices Act of 1977, that the right to privacy is a personal and fundamental right protected by article I, section 1 of the Constitution of California and by the United States Constitution, and that all individuals have a right of privacy in information pertaining to them. (Civ. Code Sec. 1798 et seq.)
- Provides, through the California Customer Records Act, requirements for the maintenance and disposal of customer records and the personal information contained therein. (Civ. Code Sec. 1798.80 et seq.)
- Requires a business that owns, licenses, or maintains personal information about a California resident to implement and maintain reasonable security procedures and practices appropriate to the nature of the information, to protect the personal information from unauthorized access, destruction, use, modification, or disclosure and requires such businesses to contractually require nonaffiliated third parties to which it discloses such personal information to similarly protect that information. (Civ. Code Sec. 1798.81.5(b), (c).)
- Requires, through the data breach notification law, that any agency, person, or business that owns or licenses computerized data that includes personal information to disclose a breach of the security of the system to any California resident whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person. The disclosure must be made in the most expedient time possible and without unreasonable delay, consistent with the legitimate needs of law enforcement, as specified. (Civ. Code Secs. 1798.29(a), (c) and 1798.82(a), (c).)
- Requires any agency, person, or business that maintains computerized data that includes personal information that the agency, person, or business does not own to notify the owner or licensee of the information of any security breach immediately following discovery if the personal information was, or is reasonably believed to have been, acquired by an unauthorized person. (Civ. Code Secs. 1798.29(b), 1798.82(b).) “Personal information” for the purposes of these provisions, means either of the following:
- an individual’s first name or first initial and the individual’s last name in combination with one or more specified data elements, such as social security number, medical information, health insurance information, or credit card number, when either the name or the data elements are not encrypted or redacted; or
- a username or email address in combination with a password or security question and answer that would permit access to an online account. (Civ. Code Secs. 1798.29(g) and (h); 1798.82(h) and (i).)
- Provides that an agency, person or business that is required to issue a security breach notification shall meet specified requirements. The notification must be written in plain language, meet certain type and format requirements, and titled “Notice of Data Breach.” The security breach notification is required to include, specified information, including a list of the types of personal information that were or are reasonably believed to have been the subject of a breach and a general description of the breach incident, if that information is possible to determine at the time the notice is provided. (Civ. Code Secs. 1798.29(d), 1798.82(d).)
- Declares any waiver of the provisions of the California Customer Records Act contrary to public policy and void and unenforceable. It provides any customer injured by a violation of these provisions a civil right of action to recover damages and authorizes injunctive relief against such businesses. Any business that violates, proposes to violate, or has violated this title may be enjoined. (Civ. Code Sec. 1798.84.)
- Provides that for a willful, intentional, or reckless violation of Section 1798.83, governing the sharing of personal information with third parties, a customer may recover a civil penalty not to exceed $3,000 per violation; otherwise, the customer may recover a civil penalty of up to $500 per violation for a violation of Section 1798.83. A prevailing plaintiff in any action commenced under Section 1798.83 shall also be entitled to recover his or her reasonable attorney’s fees and costs. (Civ. Code Sec. 1798.84.)
This bill:
- Provides that a consumer credit reporting agency (CCRA), as defined, that owns, licenses, or maintains personal information about a California resident, or a third party that maintains such information on behalf of the CCRA, that knows, or reasonably should know, that a computer system it owns, operates, or maintains, and for which it controls the security protocols, as defined, is subject to a security vulnerability that poses a significant risk to the security of computerized data that contains personal information, as defined, shall do all of the following:
- if a CCRA knows or reasonably should know that a software update is available to address the vulnerability, it shall begin the necessary testing, planning, and assessment of its systems for implementation of that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware, or after the point at which it reasonably should have become aware, of the vulnerability and the available software update. The software update shall be completed in the same manner, but in any case no later than 90 days thereafter;
- until the software update is complete, the CCRA shall employ reasonable compensating controls, as defined, to reduce the risk of a breach caused by the vulnerability; and
- notwithstanding whether a software update is available, the CCRA shall identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited. It must also test and evaluate the impact of compensating controls and software updates and how they affect the vulnerability of the system to threats to the security of computerized data and must contractually require that the third party implement and maintain appropriate security measures for personal information.
- Provides that the Attorney General has exclusive authority to enforce this section.
- Defines “significant risk” as a vulnerability score, calculated using a standard measurement system that is accepted as a best practice for the industry, to determine that the risk could reasonably result in a breach of the security of the system of personal information.
Background
“If you have a credit report, there’s a good chance that you’re one of the 143 million American consumers whose sensitive personal information was exposed in a data breach at Equifax, one of the nation’s three major credit reporting agencies.” (Seena Gressin, The Equifax Data Breach: What to Do (Sep. 9, 2017) Federal Trade Commission <https://www.consumer.ftc.gov/blog/2017/09/equifax-data-breach-what-do [as of June 4, 2018].) The infamous breach at Equifax lasted at least several months in 2017. The hackers involved were able to access people’s names, Social Security numbers, birth dates, addresses, and driver’s license numbers. Over 200,000 consumers also had their credit card numbers stolen.
There is evidence that the massive hack of personal information has led to extensive identity theft with the thieves using the stolen information to apply for mortgages, credit cards, and student loans. The information is also being used to tap into bank accounts, to file insurance claims, and to incur massive debts on behalf of affected consumers. A nation-wide class action suit has been filed against Equifax, Allen et al. v. Equifax, which alleges the company “failed spectacularly” in its legal responsibilities to protect consumers’ confidential data. It also alleges that the company failed to take steps to upgrade its security protocols, such as installing a remedial patch provided by a software maker, and then delayed informing consumers about the breach, thereby preventing them from taking steps to minimize the damage.
Recently, Equifax’s former chief executive officer admitted that the company did not meet its responsibility to protect sensitive consumer information, confirming that the failure to fix a software vulnerability led to the massive, unprecedented theft of personal data. The company was using open source Apache software. Months before hackers breached Equifax’s system, the Apache Software Foundation issued a “patch” to address the security vulnerability in the software.
In fact, the Department of Homeland Security specifically notified Equifax of the vulnerability in its software and the need for the patch. Following up on this, the company’s own security team required the vulnerability be patched with 48 hours. That never happened, and, as a result, half of the people in the United States had their personal information stolen.
This bill places requirements on consumer credit reporting agencies, and affiliated third parties, that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of the data it contains. Such entities are required to begin to implement software updates, if available, in a timely manner, and to identify and respond to security vulnerabilities in order to mitigate the attendant risks.
Comments
The author writes:
According to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers’ personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats.
AB 1859 attempts to do this by requiring a CCRA conducting business in California to begin to implement a patch of its computer system within three days, and then complete the installation within the most expedient time possible, consistent with industry best practices, but no longer than [90] days in any case, if it is subject to a vulnerability that could compromise the security of computerized data containing personal information
Ensuring security vulnerabilities are addressed in a timely and effective manner
California recognizes that the right to privacy is a fundamental right, and has enshrined that right along with other fundamental rights in Article I, Section 1 of the California Constitution.
Unfortunately, because of the size of its economy and the sheer number of consumers, the data collected and held by California businesses is frequently targeted by cyber criminals. Over the four-year period from 2012 to 2015, the Attorney General received reports on over 657 breaches, affecting over 49 million records. (California Department of Justice, California Data Breach Report (Feb. 2016) <https://oag.ca.gov/breachreport 2016 [as of June 7, 2018].) In 2015 alone, nearly three in five Californians were victims of a data breach. These data breaches are not harmless. The Attorney General reports that in 2014, 67 percent of breach victims in the United States were also victims of fraud.
Existing law requires businesses that own, license, or maintain certain personal information to implement and maintain reasonable security procedures and practices to protect that information. (Civ. Code Sec. 1798.81.5.) In the event that such personal information of a California resident has been acquired by an unauthorized person, the responsible business is required to disclose such a breach to the affected person in the most expedient time possible and without unreasonable delay. (Civ. Code Sec. 1798.82.)
This bill builds on this statutory scheme. It requires CCRAs, and affiliated third parties, that handle the personal information of California residents to address security vulnerabilities that they know, or reasonably should know, exist. It requires these entities to take action in a reasonably timely manner, as specified, in response to such threats. It also requires these companies to proactively mitigate the security issues and to prioritize and address the vulnerabilities, regardless of the availability of a “patch” for the software.
This is a modest, commonsense requirement that should arguably already be taking place as part of baseline information security. Furthermore, it narrowly targets security risks that pose a “significant risk.” This bill helps to ensure that there is not another easily preventable breach like that in the Equifax context. Recent amendments remove the ability of consumers to enforce the protections this bill affords them, and instead places exclusive authority for enforcement with the Attorney General.
FISCAL EFFECT: Appropriation: Fiscal Com.: Local:
According to the Senate Appropriations Committee, negligible fiscal impact to the state.
Insurance Commissioner Dave Jones
California Low-Income Consumer Coalition
Privacy Rights Clearinghouse
OPPOSITION: (Verified 8/17/18)
California Association of Collectors
Consumer Data Industry Association
ARGUMENTS IN SUPPORT: The California Low-Income Consumer Coalition writes in support: “CCRAs assemble consumer financial information for the purpose of issuing credit reports to third parties. The credit reports contain a historical record of the debts and associated payment information of individuals. Credit file information, which helps generate a score, is most commonly used to help lenders assess the risk of potential borrowers when underwriting a loan. Credit reports are also used by landlords when evaluating potential tenants and by employers when evaluating potential employees. These reports and the data contained therein need enhanced protections given the potential challenges consumers may face in the event of a beach. . . . AB 1859 updates our law to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats.”
ARGUMENTS IN OPPOSITION: The Consumer Data Industry Association “objects to the bill for several reasons. First, CCRAs already are required to adhere to high data protection standards set in federal statutes and rules, national standards, and self-imposed best practices. Second, the bill should not single out CCRAs for special data protection standards when there are plenty of other businesses that handle the same sensitive, personal information processed by CCRAs. Third, in the event of a violation of existing, robust laws, there are substantial procedures to enforce those laws.”
ASSEMBLY FLOOR: 57-15, 5/31/18
AYES: Acosta, Aguiar-Curry, Arambula, Baker, Berman, Bloom, Bonta, Burke, Caballero, Calderon, Carrillo, Cervantes, Chau, Chiu, Chu, Cooley, Cooper, Daly, Eggman, Frazier, Friedman, Cristina Garcia, Eduardo Garcia, Gipson, Gloria, Gonzalez Fletcher, Gray, Grayson, Holden, Irwin, Jones-Sawyer, Kalra, Kamlager-Dove, Lackey, Levine, Limón, Low, Maienschein, McCarty, Medina, Melendez, Mullin, Muratsuchi, Nazarian, Obernolte, Quirk, Reyes, Rodriguez, Salas, Santiago, Mark Stone, Thurmond, Ting, Waldron, Weber, Wood, Rendon
NOES: Travis Allen, Bigelow, Brough, Chávez, Cunningham, Flora, Fong, Gallagher, Harper, Kiley, Mathis, Mayes, Patterson, Steinorth, Voepel
NO VOTE RECORDED: Chen, Choi, Dahle, O'Donnell, Quirk-Silva, Rubio
8/20/18 9:57:49
**** END ****
SENATE COMMITTEE ON
Senator Anthony Portantino, Chair
2017 - 2018 Regular Session
AB 1859 (Chau) - Customer records
Version: | Policy Vote: |
Urgency: | Mandate: |
Hearing Date: | Consultant: |
Bill Summary:
AB 1859 would require a consumer credit reporting agency (CCRA) to patch vulnerable computer systems it owns, operates, or maintains. It also would allow a California resident whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person because of the breach to recover a civil penalty for each breach, damages, and reasonable attorney’s fees and costs.
*********** ANALYSIS ADDENDUM – SUSPENSE FILE ***********
The following information is revised to reflect amendments
adopted by the committee on August 16, 2018
Fiscal Impact:
Negligible fiscal impact to the state.
Author Amendments:
Limit the scope to only national CCRAs, extend timeframe to patch vulnerabilities, and limit enforcement of the provisions of this measure to only by the Attorney General.
-- END --
SENATE COMMITTEE ON APPROPRIATIONS
Senator Anthony Portantino, Chair
2017 - 2018 Regular Session
AB 1859 (Chau) - Customer records
Version: May 3, 2018 | Policy Vote: JUD. 5 - 2 |
Urgency: No | Mandate: No |
Hearing Date: August 6, 2018 | Consultant: Shaun Naidu |
This bill meets the criteria for referral to the Suspense File.
Bill Summary:
AB 1859 would require a consumer credit reporting agency (CCRA) to patch vulnerable computer systems it owns, operates, or maintains. It also would allow a California resident whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person because of the breach to recover a civil penalty for each breach, damages, and reasonable attorney’s fees and costs.
Fiscal Impact:
Unknown, potentially-significant workload cost pressures to the court to adjudicate lawsuits filed because of unauthorized access to personal information because of a breach, as specified, that otherwise would not have been filed absent the ability to seek the civil penalty and damages provided by this bill. While the superior courts are not funded on a workload basis, an increase in workload could result in delayed court services and would put pressure on the General Fund to fund additional staff and resources. For example, the 2018 Budget Act appropriated $64 million from the General Fund to backfill continued reduction in fine and penalty revenue for trial court operations. (General Fund*)
*Trial Court Trust Fund
Background:
It is the intent of the Legislature to ensure that personal information about California residents is protected. To that end, the Legislature has enacted certain provisions of law to encourage business that own, license, or maintain personal information about Californians to provide reasonable security for that information. Specifically, a business that owns, licenses, or maintains personal information about a California resident shall implement and maintain reasonable security procedures and practices appropriate to the nature of the information, to protect the personal information from unauthorized access, destruction, use, modification, or disclosure. Additionally, a business is required to take all reasonable steps to dispose of customer records containing personal information and must comply with other requirements on a business relating to the custody of customer records containing personal information. “Personal information” is defined as any information that identifies, relates to, describes, or is capable of being associated with, a particular individual, including, but not limited to, his or her name, signature, social security number, physical characteristics or description, address, telephone number, passport number, driver’s license or state identification card number, insurance policy number, education, employment, employment history, bank account number, credit card number, debit card number, or any other financial information, medical information, or health insurance information but does not include publicly-available information that is lawfully made available to the general public from federal, state, or local government records.
Proposed Law:
This bill would require a CCRA that owns, licenses, or maintains personal information about a California resident (and any entity that has a contract with a CCRA and maintains personal information about a California resident on behalf of the CCRA) that knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information, to take certain measures to protect that data. These measures including implementing software updates, if the CCRA or contractor knows or reasonably should know that a software update is available to address the security vulnerability, and employing reasonable mitigation measures to reduce the risk of a breach caused by computer system vulnerability until the software update is complete, as specified.
Additionally, AB 1859 would allow a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as specified, as a result of a breach of the security of the system caused, in whole or in part, by a security vulnerability that was not addressed as required, to bring a civil action to recover damages, civil penalties, and reasonable attorney’s fees and costs for that injury. This measure would a person to also recover civil penalties for a willful, intentional, or reckless violation of the bill’s provisions.
Related Legislation:
SB 1121 (Dodd, 2018) would expand the California Customer Records Act to apply to consumers and would allow for a new cause of action. SB 1121 is pending on the Assembly floor.
SB 1196 (Jackson, 2018) would allow a person whose personal identifying information has been used unlawfully in a business entity filing to petition a court for an order directing that the information be redacted or otherwise labeled as impersonated and requiring the removal of the personal identifying information from publicly-accessible electronic indexes and databases. SB 1196 is pending in the Assembly Committee on Appropriations.
Staff Comments:
As stated in the analysis of this bill by the Senate Committee on Judiciary:
“If you have a credit report, there’s a good chance that you’re one of the 143 million American consumers whose sensitive personal information was exposed in a data breach at Equifax, one of the nation’s three major credit reporting agencies.” (Seena Gressin, The Equifax Data Breach: What to Do (Sep. 9, 2017) Federal Trade Commission <https://www.consumer.ftc.gov/blog/2017/09/equifax-data-breach-what-do> [as of June 4, 2018].) The infamous breach at Equifax lasted at least several months in 2017. The hackers involved were able to access people’s names, Social Security numbers, birth dates, addresses, and driver’s license numbers. Over 200,000 consumers also had their credit card numbers stolen.
There is evidence that the massive hack of personal information has led to extensive identity theft with the thieves using the stolen information to apply for mortgages, credit cards, and student loans. The information is also being used to tap into bank accounts, to file insurance claims, and to incur massive debts on behalf of affected consumers. A nation-wide class action suit has been filed against Equifax, Allen et al. v. Equifax, which alleges the company “failed spectacularly” in its legal responsibilities to protect consumers’ confidential data. It also alleges that the company failed to take steps to upgrade its security protocols, such as installing a remedial patch provided by a software maker, and then delayed informing consumers about the breach, thereby preventing them from taking steps to minimize the damage.
While the California Customer Records Act provides protections and legal remedies for “customers,” the individuals whose information was accessed by unauthorized persons in the Equifax breach were not customers of the CCRA and therefore are not able to pursue legal action under that act. This bill would allow any California resident whose personal information was acquired by an unauthorized person because of the breach that was caused by an unaddressed security vulnerability to pursue a civil action because of that harm. Consequently, this bill would create a new cause of action that could lead to additional filings of civil cases that the court would have to adjudicate.
The actual fiscal impact of AB 1859 will depend on many factors, including the number of breaches of CCRA computer systems because of unaddressed security vulnerabilities that occur, if a resident chooses to pursue legal action, if there are alternative remedies available to a resident, and the factors unique to each case. While it is unknown how many petitions would be filed ultimately, it costs the court $7,010 in personnel and resources to operate a courtroom for one day. This cost takes into consideration the time from when a petition or complaint is received by the court, processing and calendaring by the clerks, any hearings presided over by a judicial officer, and the finalizing of the outcome by the clerk. Additionally, it costs the court, on average, a little over $11,600 in personnel and resources to adjudicate an unlimited civil case, which likely would be the type of case litigation brought pursuant to this bill would be if it proceeded as a class action. If breaches of CCRA computer systems that resulted in the unauthorized access to the personal information of California residents led to the filing of more than four new large cases, or a few complex cases that took longer than seven days to adjudicate, the cost pressures to the court would surpass the Suspense File threshold. As indicated above, while the court is not funded on a workload basis, an increase in workload could result in delayed court services and would put pressure on the General Fund to fund additional staff and resources.
-- END --
Senator Hannah-Beth Jackson, Chair
2017-2018 Regular Session
Bill No: AB 1859 (Author:Chau)
Version: May 3, 2018
Hearing Date: June 26, 2018
Fiscal: No
Urgency: No
Consultant: CK
SUBJECT
Customer records
DESCRIPTION
This bill would place requirements on consumer credit reporting agencies, and affiliated contracting entities, that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of the personal information it contains. Such entities would be required to implement software updates, if available, in a timely manner, and to identify and respond to security vulnerabilities in order to mitigate the attendant risks. California residents would be afforded a cause of action for breaches that result from a company’s failure to follow these modest measures.
BACKGROUND
“If you have a credit report, there’s a good chance that you’re one of the 143 million American consumers whose sensitive personal information was exposed in a data breach at Equifax, one of the nation’s three major credit reporting agencies.” (Seena Gressin, The Equifax Data Breach: What to Do (Sep. 9, 2017) Federal Trade Commission <https://www.consumer.ftc.gov/blog/2017/09/equifax-data-breach-what-do> [as of June 4, 2018].) The infamous breach at Equifax lasted at least several months in 2017. The hackers involved were able to access people’s names, Social Security numbers, birth dates, addresses, and driver’s license numbers. Over 200,000 consumers also had their credit card numbers stolen.
There is evidence that the massive hack of personal information has led to extensive identity theft with the thieves using the stolen information to apply for mortgages, credit cards, and student loans. The information is also being used to tap into bank accounts, to file insurance claims, and to incur massive debts on behalf of affected consumers. A nation-wide class action suit has been filed against Equifax, Allen et al. v. Equifax, which alleges the company “failed spectacularly” in its legal responsibilities to protect consumers’ confidential data. It also alleges that the company failed to take steps to upgrade its security protocols, such as installing a remedial patch provided by a software maker, and then delayed informing consumers about the breach, thereby preventing them from taking steps to minimize the damage.
Recently, Equifax’s former chief executive officer admitted that the company did not meet its responsibility to protect sensitive consumer information, confirming that the failure to fix a software vulnerability led to the massive, unprecedented theft of personal data. The company was using open source Apache software. Months before hackers breached Equifax’s system, the Apache Software Foundation issued a “patch” to address the security vulnerability in the software.
In fact, the Department of Homeland Security specifically notified Equifax of the vulnerability in its software and the need for the patch. Following up on this, the company’s own security team required the vulnerability be patched with 48 hours. That never happened, and, as a result, half of the people in the United States had their personal information stolen.
This bill would place requirements on consumer credit reporting agencies, and affiliated contractors, that know, or reasonably should know, that one of their computer systems is subject to a security vulnerability that poses a significant risk to the security of the data it contains. Such entities would be required to implement software updates, if available, in a timely manner, and to identify and respond to security vulnerabilities in order to mitigate the attendant risks. California residents would be afforded a cause of action for breaches that result from a company’s failure to follow these modest measures.
CHANGES TO EXISTING LAW
Existing law, the Information Practices Act of 1977, declares that the right to privacy is a personal and fundamental right protected by article I, section 1 of the Constitution of California and by the United States Constitution, and that all individuals have a right of privacy in information pertaining to them. It further states the following legislative findings:
- the right to privacy is being threatened by the indiscriminate collection, maintenance, and dissemination of personal information and the lack of effective laws and legal remedies;
- the increasing use of computers and other sophisticated information technology has greatly magnified the potential risk to individual privacy that can occur from the maintenance of personal information; and
- in order to protect the privacy of individuals, it is necessary that the maintenance and dissemination of personal information be subject to strict limits. (Civ. Code Sec. 1798 et seq.)
Existing law, the California Customer Records Act, provides requirements for the maintenance and disposal of customer records and the personal information contained therein. It provides definitions including the following:
- “records” means any material, regardless of the physical form, on which information is recorded or preserved by any means, including in written or spoken words, graphically depicted, printed, or electromagnetically transmitted. “Records” does not include publicly available directories containing information an individual has voluntarily consented to have publicly disseminated or listed, such as name, address, or telephone number;
- “customer” means an individual who provides personal information to a business for the purpose of purchasing or leasing a product or obtaining a service from the business;
- “individual” means a natural person; and
- “personal information” means any information that identifies, relates to, describes, or is capable of being associated with, a particular individual, including, but not limited to, his or her name, signature, social security number, physical characteristics or description, address, telephone number, passport number, driver’s license or state identification card number, insurance policy number, education, employment, employment history, bank account number, credit card number, debit card number, or any other financial information, medical information, or health insurance information. “Personal information” does not include publicly available information that is lawfully made available to the general public from federal, state, or local government records. (Civ. Code Sec. 1798.80 et seq.)
Existing law requires a business that owns, licenses, or maintains personal information about a California resident to implement and maintain reasonable security procedures and practices appropriate to the nature of the information, to protect the personal information from unauthorized access, destruction, use, modification, or disclosure and requires such businesses to contractually require nonaffiliated third parties to which it discloses such personal information to similarly protect that information. (Civ. Code Sec. 1798.81.5(b), (c).)
Existing law, the data breach notification law, requires any agency, person, or business that owns or licenses computerized data that includes personal information to disclose a breach of the security of the system to any California resident whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person. The disclosure must be made in the most expedient time possible and without unreasonable delay, consistent with the legitimate needs of law enforcement, as specified. (Civ. Code Secs. 1798.29(a), (c) and 1798.82(a), (c).)
Existing law requires any agency, person, or business that maintains computerized data that includes personal information that the agency, person, or business does not own to notify the owner or licensee of the information of any security breach immediately following discovery if the personal information was, or is reasonably believed to have been, acquired by an unauthorized person. (Civ. Code Secs. 1798.29(b), 1798.82(b).) “Personal information” for the purposes of these provisions, means either of the following:
- an individual’s first name or first initial and the individual’s last name in combination with one or more specified data elements, such as social security number, medical information, health insurance information, or credit card number, when either the name or the data elements are not encrypted or redacted; or
- a username or email address in combination with a password or security question and answer that would permit access to an online account. (Civ. Code Secs. 1798.29(g) and (h); 1798.82(h) and (i).)
Existing law provides that an agency, person or business that is required to issue a security breach notification shall meet specified requirements. The notification must be written in plain language, meet certain type and format requirements, and titled “Notice of Data Breach.” The security breach notification shall include, under specified headings, the following information:
- the name and contact information of the reporting person or business subject to this section;
- a list of the types of personal information that were or are reasonably believed to have been the subject of a breach;
- if the information is possible to determine at the time the notice is provided, then any of the following: (i) the date of the breach, (ii) the estimated date of the breach, or (iii) the date range within which the breach occurred. The notification shall also include the date of the notice;
- whether notification was delayed as a result of a law enforcement investigation, if that information is possible to determine at the time the notice is provided;
- a general description of the breach incident, if that information is possible to determine at the time the notice is provided;
- the toll-free telephone numbers and addresses of the major credit reporting agencies if the breach exposed a social security number or a driver’s license or California identification card number;
- if it is a person or business providing the notification and the person or business was the source of the breach, an offer to provide appropriate identity theft prevention and mitigation services, which must be provided at no cost to the affected person for not less than 12 months along with all information necessary to take advantage of the offer to any person whose information was or may have been breached if the breach exposed or may have exposed specified personal information. (Civ. Code Secs. 1798.29(d), 1798.82(d).)
Existing law authorizes an agency, person, or business to also include in the security breach notification any of the following:
- information about what the person or business has done to protect individuals whose information has been breached; or
- advice on steps that the person whose information has been breached may take to protect himself or herself. (Civ. Code Secs. 1798.29(d), 1798.82(d).)
Existing law declares any waiver of the provisions of the California Customer Records Act contrary to public policy and void and unenforceable. It provides any customer injured by a violation of these provisions a civil right of action to recover damages and authorizes injunctive relief against such businesses. Any business that violates, proposes to violate, or has violated this title may be enjoined. (Civ. Code Sec. 1798.84.)
Existing law provides that for a willful, intentional, or reckless violation of Section 1798.83, governing the sharing of personal information with third parties, a customer may recover a civil penalty not to exceed $3,000 per violation; otherwise, the customer may recover a civil penalty of up to $500 per violation for a violation of Section 1798.83. A prevailing plaintiff in any action commenced under Section 1798.83 shall also be entitled to recover his or her reasonable attorney’s fees and costs. (Civ. Code Sec. 1798.84.)
This bill would provide that a consumer credit reporting agency (CCRA) that owns, licenses, or maintains personal information about a California resident, or an entity that has a contract with a CCRA and maintains such information on behalf of the CCRA, that knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a security vulnerability that poses a significant risk to the
security of computerized data within the system that contains personal information,
as defined in subdivision (h) of Section 1798.82, shall do all of the following:
- if a CCRA knows or reasonably should know that a software update is available to address the vulnerability, it shall begin to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware of the vulnerability and the available software update. The software update shall be completed in the same manner, but in any case no later than 30 days after becoming aware of the vulnerability and the available software update;
- until the software update is complete, the CCRA shall employ reasonable mitigation measures to reduce the risk of a breach caused by the vulnerability;
- notwithstanding whether a software update is available, the CCRA shall identify, prioritize, and address the highest-risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities that pose the greatest security risk will be exploited. It must also test the impact of mitigation measures and software updates on its computer system and how they affect the vulnerability of the system to threats to the security of computerized data.
This bill would provide that a California resident whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as described in subdivision (a) of Section 1798.82, as a result of a breach of the security of the system caused, in whole or in part, by a security vulnerability that was not addressed, as required by this bill, is deemed to have suffered an injury in fact, and, therefore, may recover a civil penalty for each breach of the security of the system, damages, and reasonable attorney’s fees and costs pursuant to Section 1798.84 in addition to any other rights or remedies provided by law.
This bill would define “significant risk” as a vulnerability score, calculated using a standard measurement system used by industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk.
COMMENT
1. Stated need for the bill
According to the author:
According to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers’ personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats.
AB 1859 attempts to do this by requiring a CCRA conducting business in California to begin to implement a patch of its computer system within three days, and then complete the installation within the most expedient time possible, consistent with industry best practices, but no longer than 30 days in any case, if it is subject to a vulnerability that could compromise the security of computerized data containing personal information. If a CCRA fails to patch its system and a data breach occurs, the bill would allow a resident of California, whose information was compromised, to bring a civil action to recover damages for his or her injuries, civil penalties for each breach of the security of the system, and reasonable attorney’s fees and costs. The specified civil penalties would be up to $500, or up to $3,000, for a willful, intentional, or reckless violation.
2. Ensuring security vulnerabilities are addressed in a timely and effective manner
California recognizes that the right to privacy is a fundamental right, and has enshrined that right along with other fundamental rights in article I, section 1 of the California Constitution.
Unfortunately, because of the size of its economy and the sheer number of consumers, the data collected and held by California businesses is frequently targeted by cyber criminals. Over the four-year period from 2012 to 2015, the Attorney General received reports on over 657 breaches, affecting over 49 million records. (California Department of Justice, California Data Breach Report (Feb. 2016) <https://oag.ca.gov/breachreport 2016> [as of June 7, 2018].) In 2015 alone, nearly three in five Californians were victims of a data breach. These data breaches are not harmless. The Attorney General reports that in 2014, 67 percent of breach victims in the United States were also victims of fraud.
Existing law requires businesses that own, license, or maintain certain personal information to implement and maintain reasonable security procedures and practices to protect that information. (Civ. Code Sec. 1798.81.5.) In the event that such personal information of a California resident has been acquired by an unauthorized person, the responsible business is required to disclose such a breach to the affected person in the most expedient time possible and without unreasonable delay. (Civ. Code Sec. 1798.82.)
This bill would build on this statutory scheme. It would require CCRAs, and affiliated contracting entities, that handle the personal information of California residents to address security vulnerabilities that they know, or reasonably should know, exist. It would require these entities to implement and complete software updates in a timely manner, as specified, in response to such threats. It would also require these companies to proactively mitigate the security issues and to prioritize and address the vulnerabilities, regardless of the availability of a “patch” for the software.
This is a commonsense requirement that should arguably already be taking place as part of baseline information security. Furthermore, it narrowly targets security risks that pose a “significant risk.” This bill would help to ensure that there is not another easily preventable breach like that in the Equifax context.
3. Incentivizing compliance with these reasonable security measures
Section 1798.84 of the Civil Code provides remedies for violations of the Customer Records Act. A customer injured by a violation can bring a civil action to recover damages or for injunctive relief. However, often it is difficult, if not impossible, to prove actual damages in many of these situations.
This bill would provide that any unauthorized access to a California resident’s personal information as a result of a security vulnerability that was not addressed pursuant to this bill’s requirements is deemed to be an injury in fact, providing the basis for a resident to bring a cause of action under Section 1798.84. For willful, intentional, or reckless violations of this bill’s provisions, a resident would be able to seek statutory penalties.
These are modest enforcement tools that will ensure companies respond to security risks before it is too late.
Support: California Low Income Consumer Coalition; Dave Jones, Insurance Commissioner; Privacy Rights Clearinghouse;
Opposition: California Association of Collectors; Consumer Data Industry Association
HISTORY
Source: Author
Related Pending Legislation:
SB 823 (Hill, 2018) would provide consumers a more expedient and accessible process for placing a security freeze on their credit report by, in part, prohibiting fees for placing, temporarily lifting, replacing, or removing such freezes; requiring prominent links be provided by CCRAs for quick, electronic control over these actions; shortening the time line for these actions; and requiring CCRAs to ensure these actions are also taken with the other CCRAs when the consumer so elects. This bill is currently in the Assembly Banking and Finance Committee.
SB 1121 (Dodd, 2018) would, in relevant part, create a more robust enforcement mechanism for violations of the Data Breach Notification law. This bill is currently in the Assembly Privacy and Consumer Protection Committee.
SB 1196 (Jackson, 2018) would authorize a person whose personal identifying information has been used unlawfully in a business entity filing to petition a court for an order directing that the information be redacted or otherwise labeled as impersonated and requiring the removal of the personal identifying information from publicly accessible electronic indexes and databases. This bill is currently in the Assembly Judiciary Committee.
AB 608 (Irwin, 2017) would prohibit consumer credit reporting agencies from charging fees in connection with placing or removing security freezes for protected consumers, defined as individuals who are under 16, incapacitated, or under a county welfare or county probation department’s jurisdiction. This bill is currently in the Senate Judiciary Committee.
Prior Legislation:
AB 241 (Dababneh, 2017) would have required a public agency that is the source of a data breach, and is required to provide affected persons with notice of the breach, to provide at least 12 months of appropriate identity theft prevention and mitigation services at no cost to the affected persons. This bill died in the Assembly Appropriations Committee.
AB 2374 (Hernández, Ch. 645, Stats. 2012) prohibited credit reporting agencies from charging specified consumers any fee for the initial placement of a security freeze, but authorized such agencies to charge a fee of up to $5 for lifting, removing, or replacing a security freeze.
AB 372 (Salas, Ch. 151, Stats. 2008) permitted a credit reporting agency to charge a fee of no more than $5 to a consumer 65 years of age or older and no more than $10 to other consumers for a request for a security freeze, removal of the freeze, or temporary lifting of the freeze for a period of time or for a specific party.
AB 2043 (Banking and Finance Committee, Ch. 521, Stats. 2006) authorized specified business entities that become the victims of identity theft to utilize debt relief protections available to natural persons who are victimized by identity theft.
AB 1294 (Wiggins, Ch. 287, Stats. 2003) required a debt collector to stop collecting a consumer’s debt if an alleged debtor provides the collector with specified information showing that the debtor is a victim of identity theft, as specified.
SB 168 (Bowen, Ch. 720, Stats. 2001) gave California consumers the right to place a freeze on their credit reports, which, while in place, prohibits a credit reporting agency from releasing the consumer’s credit report without the express authorization of the consumer.
AB 156 (Murray, Ch. 768, Stats. 1997) formally recognized identity theft as a crime, providing that it is a misdemeanor for a person to willfully obtain personal identifying information of another and use that information to obtain, or attempt to obtain, credit, goods, or services in the name of another person without the consent of that person.
Prior Vote:
Assembly Floor (Ayes 57, Noes 15)
Assembly Judiciary Committee (Ayes 8, Noes 2)
Assembly Privacy and Consumer Protection Committee (Ayes 9, Noes 1)
**************
ASSEMBLY THIRD READING
ATR Bill Id:AB 1859
Author:(Chau)
As Amended Ver:May 3, 2018
Majority vote
Committee | Votes | Ayes | Noes |
Privacy | 9-1 | Chau, Baker, Berman, Calderon, Irwin, Mullin, Obernolte, Reyes, Ting | Kiley |
Judiciary | 8-2 | Mark Stone, Chau, Chiu, Gonzalez Fletcher, Holden, Kalra, Maienschein, Reyes | Cunningham, Kiley |
SUMMARY: Creates a liability provision for a consumer credit reporting agency (CCRA), or an entity under contract with the CCRA, for failure to address a known security vulnerability in a computer system it owns or operates when the vulnerability causes a breach of the system that comprises the personal information of a resident of California. Specifically, this bill:
- Provides that a CCRA that owns, licenses, or maintains personal information about a California resident, or an entity under contract with the CCRA and maintains personal information about a California resident on behalf of the CCRA, that knows or reasonably should know, that a computer system it owns, operates, or maintains is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information to do all of the following:
- Begin, if the consumer credit reporting agency knows or reasonably should know that a software update is available to address a known security vulnerability, to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than three business days after becoming aware of the vulnerability and the available software update, and complete the update within 30 days.
- In keeping with industry best practices, employ reasonable mitigation measures to reduce the risk of a breach caused by a computer system vulnerability until the software update described in a), above, is complete.
- Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do both of the following:
- Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities which pose the greatest security risk will be exploited.
- Test the impact of mitigation measures and software updates on its computer system and how they affect the vulnerability of the system to the security of computerized data.
- Defines the term "significant risk" to mean the following: a vulnerability score, calculated using a standard measurement system industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk.
- Permits recovery of damages, if proven, as well as a civil penalty for each breach of the security system to a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person as a result of a breach of the security of the system that was caused, in whole or in part, by an unaddressed computer system security vulnerability that was not addressed as required by 1), above.
FISCAL EFFECT: Unknown. This bill is keyed non-fiscal by the Legislative Counsel.
COMMENTS: According to the author, "According to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers' personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats. That is what this bill attempts to do."
ARGUMENTS IN SUPPORT: Supporters of the bill cite the Equifax breach as an example of the need for the bill and raise concerns regarding the lack of accountability under current law for CCRAs in relation to the amount of sensitive personal information that they hold. The California Low Income Consumer Coalition states:
CCRAs assemble consumer financial information for the purpose of issuing credit reports to third parties. The credit reports contain a historical record of the debts and associated payment information of individuals. Credit file information, which helps generate a score, is most commonly used to help lenders assess the risk of potential borrowers when underwriting a loan. Credit reports are also used by landlords when evaluating potential tenants and by employers when evaluating potential employees. These reports and the data contained therein need enhanced protections given the potential challenges consumers may face in the event of a beach.
Privacy Rights Clearinghouse, also in support, explains, "The US Department of Homeland Security, Computer Emergency Readiness Team (U.S. CERT) notified Equifax of the need to patch a security vulnerability in its Apache Struts software on March 8, 2017. However, Equifax failed to patch this software in a timely manner. As a result, between May 13 and July 30, 2017, hackers accessed sensitive personal information by exploiting the Apache Struts vulnerability. The breach gave criminals access to consumer names, Social Security numbers, birth dates, addresses, and in some instances, driver's license numbers and credit card numbers – all the data needed for fraudsters to commit identity theft."
ARGUMENTS IN OPPOSITION: The Consumer Data Industry Association (CDIA) argues in opposition that "Assembly Bill 1859 is inaccurately premised upon the belief that software updates (often called patches) are magic solutions to prevent breaches. Yet a forced patch without mitigating controls and proper testing could create greater security risks and system disruptions, and often to consumer disturbance. While we do not believe that the bill intends such economic disruptions and consumer disturbances, that is the practical effect on consumers and industry."
CDIA further argues CCRAs are already required to adhere to high data protection standards in federal statutes, rules, national standards, and self-imposed best practices. CDIA argues that this bill singles out CCRAs when many different type of businesses handle consumers' personal information and are vulnerable to data breach. Finally, CDIA contends that there are substantial methods to enforce violations of existing law. CDIA writes, "This bill is viewed through the lens of the Equifax breach, which was announced in September 2017. There is a strong desire by all businesses, including Equifax, to never have a similar criminal attack invade a data system. CCRAs must adhere to the federal Fair Credit Reporting Act (FCRA), the state fair credit reporting act (CCRAA), the Safeguards Rule of the federal Gramm-Leach-Bliley Act (GLBA), and the state breach notification law. It is possible that laws were violated leading up to and following the Equifax breach. Possible violations are currently being investigated by state attorneys general, the FTC, and the CFPB, and claims are being litigated by over 200 putative class action lawsuits."
Analysis Prepared by: Nichole Rapier / P. & C.P. / (916) 319-2200 FN: 0002817
Date of Hearing: May 1, 2018
ASSEMBLY COMMITTEE ON
, Chair
ABPCA Bill Id:
Author:() – As Amended Ver:
As Proposed to be Amended
SUBJECT:
KEY ISSUE: Should a consumer credit reporting agency (CCRA), or an entity under contract with the CCRA that maintains personal information about the CCRA’s customers, be liable for a breach of its computer system caused by a known securIty vulnerability in the system that the CCRA or its contractor failed to address and where the vulnerability caused a breach of the system, resulting in the disclosure of a customer’s personal information?
SYNOPSIS
Under current law an individual may recover damages for a violation by a consumer credit reporting agency (CCRA) of the Information Practices Act (Civil Code Section 1798), such as the requirement for a CCRA to promptly notify its customers of a data breach. However, no provision of the Act requires a CCRA to take proactive steps to remediate a suspected vulnerability in their security system to avoid a data breach, even if the vulnerability is known and a remedy for the vulnerability is possible. In 2017, Equifax experienced a security breach, lasting from mid-May through July, exposing 145.5 million people in the United States to a compromise of their personal information. According to the Federal Trade Commission, the hackers accessed names, Social Security numbers, birth dates, addresses and, in some instances, driver’s license numbers. They also stole credit card numbers for about 209,000 people and dispute documents with personal identifying information of about 182,000 people. Companies such as Equifax should have an obligation to respond to the vulnerabilities in their system prior to a breach of this nature.
This bill responds to the information uncovered in the investigation of the Equifax breach that consumer credit reporting agencies failed to protect its computer system from hackers, despite known and fixable vulnerabilities in the Equifax computer system. The bill requires a CCRA or other entity contracted with a CCRA that knows or reasonably should know that a software update is available to address a known security vulnerability. It requires a CCRA to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 3 business days after becoming aware of the vulnerability and the available software update, and complete the update within 30 days. It also outlines required intermediary measures while the repairs are being implemented and mitigation to reduce the vulnerability for the customer or resident. It creates the right for an individual whose information was compromised to bring a civil action to recover damages for his or her injuries, civil penalties, and reasonable attorney’s fees and costs.
This bill is author-sponsored and is supported by the California Low Income Consumer Coalition and Privacy Rights Clearinghouse. The Civil Justice Association of California opposes the bill, unless amended, and the Consumer Data Industry Association opposes the bill. This bill was passed out of the Assembly Privacy and Consumer Protection Committee on a 9-1 vote.
SUMMARY: Creates a liability provision for a consumer credit reporting agency (CCRA), or an entity under contract with the CCRA, for failure to address a known security vulnerability in a computer system it owns or operates when the vulnerability causes a breach of the system that comprises the personal information of a resident of California. Specifically, this bill:
- Provides that a CCRA that owns, licenses, or maintains personal information about a California resident, or an entity under contract with the CCRA and maintains personal information about a California resident on behalf of the CCRA, that knows or reasonably should know, that a computer system it owns, operates, or maintains is subject to a security vulnerability that poses a significant risk to the security of computerized data within the system that contains personal information to do all of the following:
- Begin, if the consumer credit reporting agency knows or reasonably should know that a software update is available to address a known security vulnerability, to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 3 business days after becoming aware of the vulnerability and the available software update, and complete the update within 30 days.
- In keeping with industry best practices, employ reasonable mitigation measures to reduce the risk of a breach caused by a computer system vulnerability until the software update described in a), above, is complete.
- Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do both of the following:
- Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities which pose the greatest security risk will be exploited.
- Test the impact of mitigation measures and software updates on its computer system and how they affect the vulnerability of the system to the security of computerized data.
- Defines the term “significant risk” to mean the following: a vulnerability score, calculated using a standard measurement system industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk.
- Permits recovery of damages, if proven, as well as a civil penalty for each breach of the security system to a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person as a result of a breach of the security of the system that was caused, in whole or in part, by an unaddressed computer system security vulnerability that was not addressed as required by 1), above.
EXISTING LAW:
- Sets forth, in the Information Practices Act, the right of an individual who is the subject of information maintained in state or local agency records to have access to that information. (Civil Code Section 1798. All further references are to this code, unless otherwise stated.)
- Requires any agency, person, or business that owns or licenses computerized data that includes personal information to disclose a breach of the security of the system to any California resident whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person and requires the disclosure to be made in the most expedient time possible and without unreasonable delay, consistent with the legitimate needs of law enforcement, as specified. (Sections 1798.29 (a), (c), 1798.82 (a), (c).)
- Requires any agency, person, or business that maintains computerized data that includes personal information that the agency, person, or business does not own to notify the owner or licensee of the information of any security breach immediately following discovery if the personal information was, or is reasonably believed to have been, acquired by an unauthorized person. (Sections 1798.29 (b), 1798.82 (b).)
- Defines “personal information,” for purposes of the breach notification statutes in 2) and 3), above, to include either a user name or email address, in combination with a password or security question and answer that would permit access to an online account, or the individual’s first name or first initial and last name in combination with one or more of the following data elements, when either the name or the data elements are not encrypted: social security number; driver’s license number or California identification card number; account number, credit or debit card number, in combination with any required security code, access code, or password that would permit access to an individual’s financial account; medical information; or health insurance information. (Sections 1798.29 (g) and (h); 1798.82 (h) and (i).)
- Clarifies that “personal information” does not include publicly available information that is lawfully made available to the general public from federal, state, or local government records. (Ibid.)
- Provides that any customer injured by a violation of Title 1.81 of the Civil Code (Section 1798 et seq., The California Customer Records Act, may institute a civil action to recover damages. (Section 1798.84 (b).)
- Designates that in addition, for a willful, intentional, or reckless violation of Section 1798.83, a customer may recover a civil penalty not to exceed three thousand dollars ($3,000) per violation; otherwise, the customer may recover a civil penalty of up to five hundred dollars ($500) per violation for a violation of Section 1798.83. (Section 1798.84 (c).)
- Permits any business that violates, proposes to violate, or has violates the title relating to Consumer Records to be enjoined. (Section 1798.84 (e).)
FISCAL EFFECT: As currently in print this bill is keyed non-fiscal.
COMMENTS: In 2017, Equifax experienced a security breach, lasting from mid-May through July, that exposed 145.5 million people in the United States to a compromise of their personal information. (Equifax Data Breach Affected 2.4 Million More Consumers, March 1, 2018, Consumer Reports.) According to the Federal Trade Commission, the hackers accessed names, Social Security numbers, birth dates, addresses and, in some instances, driver’s license numbers. They also stole credit card numbers for about 209,000 people and dispute documents with personal identifying information of about 182,000 people.
This bill responds to the information discovered in the investigation of the Equifax breach that consumer credit reporting agencies failed to protect its computer system from hackers, despite known vulnerabilities in that system. The goal of the bill is to safeguard the computer systems of CCRAs, and more importantly the personal information within those systems, by requiring CCRAs to take proactive steps in response to known security vulnerabilities in their security systems. If the consumer credit reporting agency or other entity contracted with a CCRA knows or reasonably should know that a software update is available to address a known security vulnerability, they are required to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case no later than 3 business days after becoming aware of the vulnerability and the available software update, and complete the update within 30 days. The CCRA or entity is also required to employ reasonable mitigation measures to reduce the risk of a breach caused by a computer system vulnerability until the software update described in a), above, is complete. Notwithstanding whether a software update is available, the consumer credit reporting agency, in keeping with industry best practices, shall do both of the following: 1) Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities which pose the greatest security risk will be exploited and 2) Test the impact of mitigation measures and software updates on its computer system and how they affect the vulnerability of the system to the security of computerized data.
It also defines “significant risk” as a vulnerability score, calculated using a standard measurement system industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk.
Finally the bill creates the right for an individual whose information was compromised to bring a civil action to recover damages for his or her injuries, civil penalties, and reasonable attorney’s fees and costs. This is an author-sponsored bill.
Regarding the need for the bill the author says:
[A]ccording to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers’ personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats. That is what this bill attempts to do.
Entities Under Contract With CCRAs. The bill in print only holds CCRAs responsible for safeguarding their own computer systems from security vulnerabilities, stating that “a consumer credit reporting agency that owns, licenses, or maintains personal information about a California resident, that knows, or reasonably should know, that a computer system it owns, operates, or maintains.” Privacy advocates raised concerns about this language, alleging that there are a great number of groups that have access to the consumer and resident information and are contracted to maintain such records.
For example, CCRAs sometimes outsource their records containing personal information about customers to cloud-based storage systems. If the cloud-based storage system is subject to a security vulnerability, that vulnerability could expose the consumer or resident information to the same risk of compromise as if the information were stored in the CCRA’s computer system itself, yet the entity operating the cloud storage system would not be subject to the requirements of the bill as it is now in print. In response to these concerns, the author has agreed to amend the bill so that the security precautions required of a CCRA would also extend to an entity under contract with the CCRA that maintains personal information about the CCRA’s customers. By extending the bill’s requirements to entities that are under contact with the CCRA for those types of services, the bill’s amended language will ensure that the consumer or resident is protected whether the vulnerability comes from the CCRA’s system, or the agent of the CCRA.
Timeframe for Implementation of Corrective Measures: As recently amended by the Assembly Privacy and Consumer Protection Committee, the bill requires that a CCRA begin to implement a software update to address a known security vulnerability “in the most expedient time possible and without unreasonable delay. . . but in any case, within 3 days of becoming aware of it.” It also requires that the update be completed within 30 days.
Opponents to the timeline have stated that “Assembly Bill 1859 is inaccurately premised upon the belief that software updates (often called patches) are magic solutions to prevent breaches. Yet a forced patch without mitigating controls and proper testing could create greater security risks and system disruptions, and often to consumer disturbance. While we do not believe that the bill intends such economic disruptions and consumer disturbances, that is the practical effect on consumers and industry.”
In its analysis of the bill, the Privacy and Consumer Protection Committee stated in response that they did not find any validity in the argument that early “patches” would create greater vulnerabilities to the system and found that implementing them was consistent with the industry practice. Also, it is worth pointing out that, as proposed to be amended, the bill clarifies that a CCRA is only required to install a software update if the CCRA knows that the update is available and that the software will address the security vulnerability in the CCRA’s computer system.
Furthermore, the bill, as it is proposed to be amended, specifies what actions a CCRA must take, in addition to or instead of installing a software update, to address the known security vulnerabilities of its computer system. The bill in print requires the CCRA to “employ reasonable mitigation measures” until a software update is available and that provision remains in the bill. But as proposed to be amended, the bill also requires the CCRA to do the following, regardless of whether a software update is available:
- Identify, prioritize, and address the highest risk security vulnerabilities most quickly in order to reduce the likelihood that the vulnerabilities which pose the greatest security risk will be exploited.
- Test the impact of mitigation measures and software updates on its computer system and how they affect the vulnerability of the system to the security of computerized data.
These proposed amendments appear to not only offer greater security protection to the CCRA’s computer systems and the personal information contained therein, but also addresses the argument of the opposition that the bill’s software update and installation requirements are a one-size-fits-all solution to the more nuanced problem of security vulnerability.
Greater Specificity about When and What Acts are Required. Under the language of the bill in print, a CCRA would be required to act when it “knows, or reasonably should know, that a computer system it owns, operates, or maintains is subject to a vulnerability that could compromise the security of computerized data that contains personal information.” This language would require that a CCRA act at every instance when there is a vulnerability to their system, regardless of the level of threat posed by the vulnerability, with no prioritization regarding to the level of threat posed by such vulnerabilities.
The U.S. Department of Commerce’s National Institute of Standards and Technologies (NIST) has established their Common Vulnerability Scoring System (CVSS) to “capture the principal characteristics of a vulnerability and produce a numerical score reflecting its severity. The numerical score can then be translated into a qualitative representation (such as low, medium, high, and critical) to help organizations properly assess and prioritize their vulnerability management processes.” (First, Common Vulnerability Scoring System – SIG, available at: https://www.first.org/cvss/; NIST, Vulnerability Metrics, available at: https://nvd.nist.gov/vuln-metrics/cvss.)
In response to the NIST’s scoring system, the author proposes to amend Section 1 of the bill to specify that a CCRA is required to address a “security vulnerability that poses a significant risk to the security” of its computer system. The author also proposes to add the following definition of “significant risk” to the bill:
As used in this section, “significant risk” means a vulnerability score, calculated using a standard measurement system industry, organization, and government information technology systems that is accepted as a best practice for the industry, to determine that the risk is elevated above the lowest level of risk.
These amendments ensure that the CCRA, and now the entities that contract with them, have proper notice and when they must act, and the provisions of the bill are far more specific.
ARGUMENTS IN SUPPORT: Supporters of the bill cite the Equifax breach as an example of the need for the bill and raise concerns regarding the lack of accountability under current law for CCRAs in relation to the amount of sensitive personal information that they hold. The California Low Income Consumer Coalition states:
CCRAs assemble consumer financial information for the purpose of issuing credit reports to third parties. The credit reports contain a historical record of the debts and associated payment information of individuals. Credit file information, which helps generate a score, is most commonly used to help lenders assess the risk of potential borrowers when underwriting a loan. Credit reports are also used by landlords when evaluating potential tenants and by employers when evaluating potential employees. These reports and the data contained therein need enhanced protections given the potential challenges consumers may face in the event of a beach.
ARGUMENTS IN OPPOSITION: Opponents of the bill have raised issues regarding certain practicality matters that the bill would raise for CCRAs including the use of “implementation” language in Section 1 as well as the ability to properly respond to the vulnerabilities within the 30 day timeframe the bill designates.
Perhaps the largest opposition to the bill is to the damages and penalties provisions that are included. The Consumer Data Industry Association laid out their concerns to this provision as follows:
First, CCRAs already are required to adhere to high data protection standards set in federal statutes and rules, national standards, and self-imposed best practices. Second, the bill should not single out CCRAs for special data protection standards when there are plenty of other businesses that handle the same sensitive, personal information processed by CCRAs. Third, in the event of a violation of existing, robust laws, there are substantial procedures to enforce those laws.
The Civil Justice Association of California (CJAC) opposes the bill (unless amended) because of its provision that allows a resident to recover a civil penalty of $500 if an unaddressed and known security vulnerability of a CCRA’s computer system results in a data breach and release of a resident’s personal information, and up to $3,000 if the breach is willful or intentional. CJAC mentions that if all 140 million affected by the Equifax breach sought the civil penalty, Equifax would be liable for $70 billion. This argument ignores the facts that not all 140 million victims were residents of California, so they could not all recover the $500 civil penalty provided by the bill. Also, the purpose of a civil penalty is to compensate victims of security breaches because actual damages in a data breach case are virtually impossible to prove. Given that data can change hands repeatedly and instantaneously, but lead to identity theft that can have consequences for years, it is hard to know who is responsible for a consumer’s actual damages. At the same time, the financial costs of data breaches to consumers are significant and real. CSID, an identity theft protection platform company that is affiliated with Experian, a CCRA, states the following about the financial and psychological costs of identity theft:
The most obvious consequence that identity theft victims encounter is financial loss, which comes in two forms: direct and indirect. Direct financial loss refers to the amount of money stolen or misused by the identity theft offender. Indirect financial loss includes any outside costs associated with identity theft, like legal fees or overdraft charges. The DOJ’s study found that victims experienced a combined average loss of $1,343. In total, identity theft victims lost a whopping $15.4 billion in 2014.
Beyond money lost, identity theft can negatively impact credit scores. While credit card companies detect a majority of credit card fraud cases, the rest can go undetected for extended periods of time. A criminal’s delinquent payments, cash loans, or even foreclosures slowly manifest into weakened credit scores. Victims often only discover the problem when they are denied for a loan or credit card application. Last year, CSID found that these types of fraud take the longest time to resolve.
Identity theft doesn’t just impact victims financially; it also often takes a significant emotional toll. A survey from the Identity Theft Research Center found that 69 percent felt fear for their personal financial security, and 65 percent felt rage or anger. And, almost 40 percent reported some sleep disruption. These feelings increased over time when victims were unable to settle the issue on their own, according to the report, which can result in problem as work or school, and add stress to relationships with friends and family.
Given these costs, the bill’s rather modest $500 civil penalty seems like a small and inadequate consequence for the consequences to consumers of a data breach.
Related Pending Legislation: SB 1121(Dodd): This bill would replace the term “customer” as used in Sections 1798.80 through 1798.84 of the Civil Code, the California Customer Records Act, with the term “consumer.” It would also provide any consumer whose personal information has been or is reasonably believed to have been breached by a violation of Section 1798.81.5 or 1798.82 with the right to institute a civil action, within four years from the time the person discovered, or should have discovered, the violation, for the recovery of statutory damages, injunctive or declaratory relief, and any other relief the court deems proper. SB 1121 was approved by the Senate Judiciary Committee on April 24th by a vote of 5-2 and has been referred to the Senate Appropriations Committee.
REGISTERED SUPPORT / OPPOSITION:
Support
California Low Income Consumer Coalition
Privacy Rights Clearinghouse
Opposition
Civil Justice Association of California (oppose unless amended)
Consumer Data Industry Association
Neutral
American Civil Liberties Union
Analysis Prepared by: Allison Adey /JUD,
Date of Hearing: April 17, 2018
ASSEMBLY COMMITTEE ON PRIVACY AND CONSUMER PROTECTION
Ed Chau, Chair
ABPCA Bill Id:AB 1859 (
Author:Chau) – As Introduced Ver:January 10, 2018
SUBJECT: Customer records
SUMMARY: This bill would require a consumer credit reporting agency (CCRA) that knows it is subject to a security vulnerability to apply applicable software updates within 10 days, and would allow residents of California to bring a civil action to recover damages in the event of a breach. Specifically, this bill would:
- Provide that a CCRA that conducts business in California, that owns, licenses, or maintains personal information about a California resident, that knows or reasonably should know, that a computer system it owns, operates, or maintains is subject to a vulnerability that could compromise the security of computerized data that contains personal information, as defined, and that also knows or reasonably should know that a software update is available to address that vulnerability, must apply that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 10 days after becoming aware of the vulnerability and the available software update.
- Provide that a resident of California whose personal information was, or is reasonably believed to have been, acquired by an unauthorized person, as a result of a breach of the security of the system caused, in whole or in part, by an unaddressed computer system vulnerability has suffered an injury in fact, and may recover a civil penalty and reasonable attorney’s fees and costs in addition to any other rights or remedies provided by law.
EXISTING LAW:
- Sets forth, in the Information Practices Act, the right of an individual who is the subject of information maintained in state or local agency records to have access to that information. (Civ. Code Sec. 1798 et seq.)
- Requires any agency, person, or business that owns or licenses computerized data that includes personal information to disclose a breach of the security of the system to any California resident whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person. The disclosure must be made in the most expedient time possible and without unreasonable delay, consistent with the legitimate needs of law enforcement, as specified. (Civ. Code Secs. 1798.29(a), (c) and 1798.82(a), (c).)
- Requires any agency, person, or business that maintains computerized data that includes personal information that the agency, person, or business does not own to notify the owner or licensee of the information of any security breach immediately following discovery if the personal information was, or is reasonably believed to have been, acquired by an unauthorized person. (Civ. Code Secs. 1798.29(b), 1798.82(b).)
- Defines “personal information,” for purposes of the breach notification statute, to include either a user name or email address, in combination with a password or security question and answer that would permit access to an online account, or the individual’s first name or first initial and last name in combination with one or more of the following data elements, when either the name or the data elements are not encrypted: social security number; driver’s license number or California identification card number; account number, credit or debit card number, in combination with any required security code, access code, or password that would permit access to an individual’s financial account; medical information; or health insurance information. “Personal information” does not include publicly available information that is lawfully made available to the general public from federal, state, or local government records. (Civ. Code Secs. 1798.29(g) and (h); 1798.82(h) and (i).)
FISCAL EFFECT: Unknown
COMMENTS:
- Purpose of this bill: In response to the Equifax breach in 2017, this bill would require any CCRA conducting business in California to patch its computer system within 10 days if it is subject to a vulnerability that could compromise the security of computerized data containing personal information. If a CCRA fails to patch its system and a data breach occurs, the bill would allow a resident of California, whose information was compromised, to bring a civil action to recover damages for his or her injuries, civil penalties, and reasonable attorney’s fees and costs. This is an author-sponsored bill.
- Author’s statement: According to the author, “According to Equifax, it experienced a cybersecurity breach from mid-May through July 2017 that resulted in the loss of 145.5 million U.S. consumers’ personal information, though this disclosure was not made until September 7, 2017. Furthermore, it has been reported by news outlets that the U.S. Department of Homeland Security (DHS) notified Equifax and other companies of a security vulnerability in their software called Apache Struts, as early as March 8, 2017. In other words, hackers had exploited the website vulnerability well after Equifax had been notified by DHS to patch its network.
The scale and severity of the Equifax breach is simply staggering and has inflicted real personal and financial costs on millions of innocent consumers for years, if not the rest of their lives. We need to examine our laws to ensure they are sufficiently updated and robust to address negligently lax behavior by credit reporting agencies when it comes to safeguarding their systems against cybersecurity threats. That is what this bill attempts to do.”
- Data breach laws and the Equifax breach: Equifax is one of the big three CCRAs, along with Experian and TransUnion. CCRAs assemble consumer financial information for the purpose of issuing credit reports to third parties. The credit reports contain a historical record of the debts and associated payment information of individuals. The information in a credit file is used to generate a credit score which serves as a quantitative metric of an individual’s credit risk, or the likelihood that the individual will pay back a loan.
Last year, Equifax suffered a cybersecurity breach caused by a website vulnerability that occurred from mid-May through July 2017. The breach gave criminals access to information including consumer names, Social Security numbers, birth dates, addresses, and in some instances, driver’s license numbers. Credit card numbers were accessed for approximately 209,000 U.S. consumers, as were documents with personal identifying information for approximately 182,000 US consumers. The breach also permitted unauthorized access to personal information for some United Kingdom and Canadian residents. On October 2, 2017, the cybersecurity firm Mandiant completed the forensic portion of the investigation into the breach and determined that 145.5 million US consumers were potentially impacted by the breach. (McCoy, USA Today, Do you want to sue Equifax over the cyberbreach? Winning a lawsuit may not be so easy (Sept. 2017) <https://www.usatoday.com/story/money/2017 /09/22/do-you-want-sue-equifax-over-cyberbreach-winning-lawsuit-may-not-so-easy/684455001/> [as of April 5, 2018].)
The Equifax breach, which affected nearly 50 percent of the total U.S. population of 323 million people, was not an isolated or limited incident. According to news reports, this breach is only the fifth largest data breach impacting U.S. consumers. (Wise, USA Today Equifax breach: Is it the biggest data breach? (Sept. 2017) < https://www.usatoday.com /story/tech/ 2017/09/07/nations-biggest-hacks-and-data-breaches-millions/644311001/>[as of April 5, 2018].) In fact, according to an Identity Theft Resource Center Data Breach Summary, there have been 273 data breaches recorded this year through April 1, and that nearly 5.5 million records have been exposed since the beginning of the year.
While no federal data breach laws exist, all 50 states, the District of Columbia, Guam, Puerto Rico and the Virgin Islands have enacted laws requiring private or governmental entities to notify individuals of security breaches involving personally identifiable information. (National Conference on State Legislatures, Security Breach Notification Laws, Updated March 29, 2018 <http://www.ncsl.org/research/telecommunications-and-information-technology/ security-breach-notification-laws.aspx> [as of April 5, 2018].) California law requires a business or state agency to notify residents whose unencrypted (or encrypted but compromised) personal information was acquired, or reasonably believed to have been acquired by an unauthorized person. (See Civ. Code Secs. 1798.29 and 1798.82.)
Last year, in response to the Equifax breach, U.S. Congressional leaders and state legislators introduced multiple pieces of legislation in response to the Equifax breach. All seven pieces of legislation introduced in Congress failed to become law amid pushback from industry groups. With consumer privacy protections stalling at the federal level, states are choosing to enact their own laws. Oregon, New York, Alabama, and Rhode Island have now joined the list of states considering new data breach legislation. Such legislation has already been proposed in Arizona, Colorado, North Carolina, and South Dakota. Much of this legislation has centered on data breach notification to consumers and the ability of consumers to initiate or lift credit freezes. This bill, instead, seeks to ensure that CCRAs take reasonable steps to protect consumers’ data before a breach occurs.
- Not all patches are created equal: When a CCRA becomes aware of a vulnerability that could compromise consumers’ personal information, this bill would generally require the CCRA to apply a software update, or “patch” within 10 days, as specified. The National Institute of Standards and Technology (NIST), under the U.S. Department of Commerce, describes “patch management” as the process for identifying, acquiring, installing, and verifying patches for products and systems. NIST writes that “[p]atches correct security and functionality problems in software and firmware. There are several challenges that complicate patch management. If organizations do not overcome these challenges, they will be unable to patch systems effectively and efficiently, leading to easily preventable compromises.” (NIST Special Publication 800-40 Revision 3, Guide to Enterprise Patch Management Technologies (July 2013) <https://nvlpubs.nist.gov/nistpubs/ SpecialPublications/NIST.SP.800-40r3.pdf> [as of April 5, 2018].) In this same guide, NIST describes how timing can further complicate patch management:
Timing, prioritization, and testing are intertwined issues for enterprise patch management. Ideally, an organization would deploy every new patch immediately to minimize the time that systems are vulnerable to the associated software flaws. However, in reality this is simply not possible because organizations have limited resources, which makes it necessary to prioritize which patches should be installed before other patches. Further complicating this is the significant risk of installing patches without first testing them, which could cause serious operational disruptions, potentially even more damaging than the corresponding security impact of not pushing the patches out. […]
There are even more issues to consider with timing. The release of a patch may provide attackers with the information that they need to exploit the corresponding vulnerability (e.g., reverse engineer the vulnerability from the patch), meaning that a newly released patch might need to be applied immediately to avoid compromises. However, if a vulnerability is not being exploited yet, organizations should carefully weigh the security risks of not patching with the operational risks of patching without first performing thorough testing.
Perhaps also useful to this conversation are the patching standards used by organizations that support credit cards, as published by the Payment Card Industry Data Security Standards (PCI-DSS). PCI-DSS requires that companies “establish a process to identify security vulnerabilities, using reputable outside sources for security vulnerability information, and assign a risk ranking (for example, as ‘high,’ ‘medium,’ or ‘low’) to newly discovered security vulnerabilities,” and offers the following guidance:
The intent of this requirement is that organizations keep up to date with new vulnerabilities that may impact their environment. Sources for vulnerability information should be trustworthy and often include vendor websites, industry news groups, mailing list, or [Rich Site Summary] RSS feeds. Once an organization identifies a vulnerability that could affect their environment, the risk that the vulnerability poses must be evaluated and ranked. The organization must therefore have a method in place to evaluate vulnerabilities on an ongoing basis and assign risk rankings to those vulnerabilities. This is not achieved by [a Approved Scanning Vendors] ASV scan or internal vulnerability scan, rather this requires a process to actively monitor industry sources for vulnerability information. Classifying the risks (for example, as ‘high,’ ‘medium,’ or ‘low’) allows organizations to identify, prioritize, and address the highest risk items more quickly and reduce the likelihood that vulnerabilities posing the greatest risk will be exploited.
There is a constant stream of attacks using widely published exploits, often called ‘zero day’ (an attack that exploits a previously unknown vulnerability), against otherwise secured systems. If the most recent patches are not implemented on critical systems as soon as possible, a malicious individual can use these exploits to attack or disable a system, or gain access to sensitive data. Prioritizing patches for critical infrastructure ensures that high-priority systems and devices are protected from vulnerabilities as soon as possible after a patch is released. Consider prioritizing patch installations such that security patches for critical or at-risk systems are installed within 30 days, and other lower-risk patches are installed within 2-3 months.
This bill, would require that all patches be applied within 10 days, regardless of the various levels of risk different vulnerabilities may pose, differing degrees of complexity, or the utility of patch management. Proponents of the bill argue that this timeline is necessary because Equifax knew of a security vulnerability, and failed to act for months, despite industry best practices and national standards. Privacy Rights Clearinghouse, in support, explains, “ The US Department of Homeland Security, Computer Emergency Readiness Team (U.S. CERT) notified Equifax of the need to patch a security vulnerability in its Apache Struts software on March 8, 2017. However, Equifax failed to patch this software in a timely manner. As a result, between May 13 and July 30, 2017, hackers accessed sensitive personal information by exploiting the Apache Struts vulnerability. The breach gave criminals access to consumer names, Social Security numbers, birth dates, addresses, and in some instances, driver’s license numbers and credit card numbers – all the data needed for fraudsters to commit identity theft.”
In contrast, the Consumer Data Industry Association (CDIA) argues in opposition that “Assembly Bill 1859 is inaccurately premised upon the belief that software updates (often called patches) are magic solutions to prevent breaches. Yet a forced patch without mitigating controls and proper testing could create greater security risks and system disruptions, and often to consumer disturbance. While we do not believe that the bill intends such economic disruptions and consumer disturbances, that is the practical effect on consumers and industry.”
Arguably, there is evidence to support the contention that installing patches prematurely is not consistent with industry best practices, in that such installation could actually increase vulnerabilities rather than decreasing them. There is also evidence to support the contention that Equifax was indeed negligent in addressing a known, high-risk vulnerability, by failing to update its software in a timely manner to address that vulnerability. Given that both of these contentions are arguably true, and given that the author’s underlying intent is to require CCRAs to act reasonably and responsibly, the author has agreed to the following amendments to create a more flexible timeline for installing patches, while still requiring CCRAs to act in a timely manner. Instead of requiring a patch to be applied within 10 days, these amendments would emphasize when a CCRA must begin the process of applying a patch, and a later date, four weeks out, by which any software patches must be installed. These amendments should ensure that CCRAs have the opportunity to adequately test and prioritize patches in an effort to reduce unintended consequences as they seek to address security vulnerabilities.
Author’s amendment:
On page 2 line 9, after “1798.82” insert: “shall do the following:
- A consumer credit reporting agency that knows or reasonably should know that a software update is available to address a vulnerability as described in subdivision (a), shall begin to implement that software update in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within three business days after becoming aware of the vulnerability and the available software update. The installation must be complete in the most expedient time possible and without unreasonable delay, in keeping with industry best practices, but in any case within 30 days after becoming aware of the vulnerability and the available software update.”
On page 2, line 9, strike “and”
On page 2, strike lines 10 – 13
On page 3, strike lines 1 - 2
On page 3, line 3, strike “(b)” and insert “(c)”
- Software patches are not the only way to address vulnerabilities: This bill would require CCRAs to apply software updates to known security vulnerabilities, or security vulnerabilities which the CCRA reasonably should have known about, within a specified timeframe. As discussed in Comment 4, above, prematurely installing patches may have the negative and unintended consequence of increasing security risks, such as providing attackers with the opportunity to reverse engineer the vulnerability from the patch. Industry experts claim that appropriate testing and timing of software updates may take anywhere from a few days to a few months depending on the complexity of the patch and the nature of the vulnerability.
Privacy advocates and industry experts alike expressed concern with the current version of the bill, which would only address software updates and not any other mitigation measures. One industry expert described the layered security framework his company employed while preparing to install the Apache Struts patch which included: firewalls, intrusion detection systems, and anti-virus malware. This layered security approach seemingly reduced risk of data breach during the weeks and months the company spent implementing the patch. Similarly, a consumer advocacy group questioned why this bill only mandated software updates, when there are many tools outside of patches that can be combined to mitigate risk and protect consumers’ data.
In addition to the amendment in Comment 4, which would create a more flexible timeline for the implementation of patches, the author has agreed to the following amendment to ensure that CCRAs employ reasonable risk mitigation measures during the implementation of any software update as would be required under this bill:
Author’s amendment:
On page 2, after new subparagraph (a)(1), insert “(2) Until the software update described in paragraph (1) is complete, the consumer credit reporting agency must, in keeping with industry best practices, employ reasonable mitigation measures to reduce the risk of a breach as caused by computer system vulnerability as described in subdivision (a).”
- Personal information stored on the cloud: A recent publication by Deloitte claimed that by the year 2020, a no-cloud policy will be as rare as a no-internet policy is today. “Cloud services globally will reach $312 billion annually by 2019, with year-over-year growth of over 15 percent. In fact, cloud services will be the fastest growing segment of IT spending as a whole as organizations begin to take advantage of the high degree of standardization, self-service functionality, and level of automation offered by paying only for what they need when they need it.” (Deloitte, Data privacy in the cloud: Navigating the new privacy regime in a cloud environment (2016) < https://www2.deloitte.com/content/dam/Deloitte/ca/ Documents/ risk/ca-en-risk-privacy-in-the-cloud-pov.PDF> [as of April 6, 2018].) Indeed, even in state government, the California Department of Technology has adopted a “cloud first” policy for when state agencies seek new information technology solutions.
Recognizing this fact, as this bill moves through the legislative process, the author may wish to consider, how to best address security vulnerabilities in the situation where a CCRA may be storing consumers’ data remotely, including the cloud.
- Additional arguments in opposition: In opposition, CDIA argues CCRAs are already required to adhere to high data protection standards in federal statutes, rules, national standards, and self-imposed best practices. CDIA argues that this bill singles out CCRAs when many different type of businesses handle consumers’ personal information and are vulnerable to data breach. CDIA writes:
CCRAs are not even close to the only companies that handle sensitive personal information. Banks and other financial institutions, insurance companies, utilities, hospitals and other health care companies, retailers, and technology companies all handle the same sensitive personal information that CCRAs do and are all potential targets for a breach. In fact, CCRAs are not the breached entity in most cases and they should not be forced to adhere to standards that do not also apply to other companies or industries with the same types of sensitive, personal information.
CDIA additionally contends that there are substantial methods to enforce violations of existing law. CDIA writes, “This bill is viewed through the lens of the Equifax breach, which was announced in September 2017. There is a strong desire by all businesses, including Equifax, to never have a similar criminal attack invade a data system. CCRAs must adhere to the federal Fair Credit Reporting Act (FCRA), the state fair credit reporting act (CCRAA), the Safeguards Rule of the federal Gramm-Leach-Bliley Act (GLBA), and the state breach notification law. It is possible that laws were violated leading up to and following the Equifax breach. Possible violations are currently being investigated by state attorneys general, the FTC, and the CFPB, and claims are being litigated by over 200 putative class action lawsuits.”
In response, the author writes “The Federal Fair Credit Reporting Act and the California Consumer Credit Reporting Agencies Act contain provisions about how to protect consumer information, such as disposing of information and ensuring customer data is handled securely, but neither of them include requirements about patching computer systems. Though the Safeguards Rule of the Gramm-Leach-Bliley Act requires businesses to implement a written information security plan and include elements to monitor, patch, and test systems and to implement mitigation controls, nothing in those provisions establish timelines by which those systems need to be patched. It is left up to each individual entity. To limit the risk of another Equifax level data breach it is imperative that we ensure Consumer Credit Reporting Agencies have clear deadlines listed in statute for when they need to patch their vulnerable security systems. AB 1859 accomplishes the goal of ensuring vulnerable computer systems are patched within a reasonable time period.”
- Private right of action, damages, and other remedies available under the law: California’s Data Breach Notification law allows customers whose information has subject to a security breach to institute a civil action to recover damages and entitles a prevailing plaintiff to recover reasonable attorney’s fees and costs. Existing law provides that these rights and remedies are cumulative to each other and to any other rights and remedies available under law. (Civ. Code Sec. 1798.98.) This bill would additionally allow a consumer whose information had been acquired in violation of the provisions of this bill to institute a civil action according to the provision described above. Civil Code Section 1798.98 authorizes a civil action per violation, which is reasonably quantifiable when applied to a data breach. If this same scheme is applied to the provisions of this bill, which sets up somewhat elastic timelines and requirements in an effort to accommodate the complexities of security vulnerabilities, authorizing a private right of action per violation creates more uncertainty. While clearly there would be a violation when a CCRA failed to apply a patch, but there is a question as to whether there would be an additional violation for each day thereafter. Similarly, how would failure to apply vulnerability-mitigation measures be treated. As such, the author may wish to amend the bill as it moves through the legislative process to more clearly specify when a consumer may bring a civil action. This should serve to create more certainty for consumers and CCRAs alike.
The Civil Justice Association of California, in opposition writes that the “inclusion of a private right of action provision could lead to artificially high level of lawsuits, motivating private trial attorneys to pursue even unwarranted claims without consequence, dragging out litigation for years. While we believe this bill has good intentions, the private right of action impedes that goal.”
- Technical amendments: The following amendments are technical in nature and offered by the author after conversations with stakeholders.
Author’s amendments:
On page 2, line 3, strike “that conducts business in California”
On page 3, line 8, strike “has” and insert “is deemed to have”
On page 3, line 8, after “and” insert “therefore”
- Double-referral: This bill is double-referred to the Assembly Judiciary Committee where it will be heard if passed by this Committee.
REGISTERED SUPPORT / OPPOSITION:
Support
California Low-Income Consumer Coalition
Privacy Rights Clearinghouse
Opposition
Civil Justice Association
Consumer Data Industry Association
Analysis Prepared by: Nichole Rapier / P. & C.P. / (916) 319-2200
Click here to enter text.
Discussed in Hearing
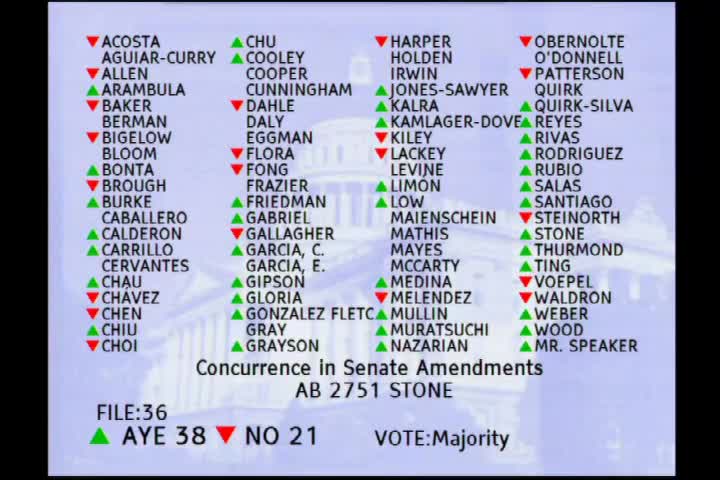 49SEC
Assembly Floor
 2MIN
Senate Floor
 1H
Senate Standing Committee on Appropriations
 4MIN
Assembly Floor
 12MIN
Assembly Standing Committee on Judiciary
 14MIN
Assembly Standing Committee on Privacy and Consumer Protection
Bill Author
Bill Co-Author(s):